dumpspedia logo
Which Linux system call loads an eBPF program and manages eBPF maps within the kernel?
Refer to the exhibit.
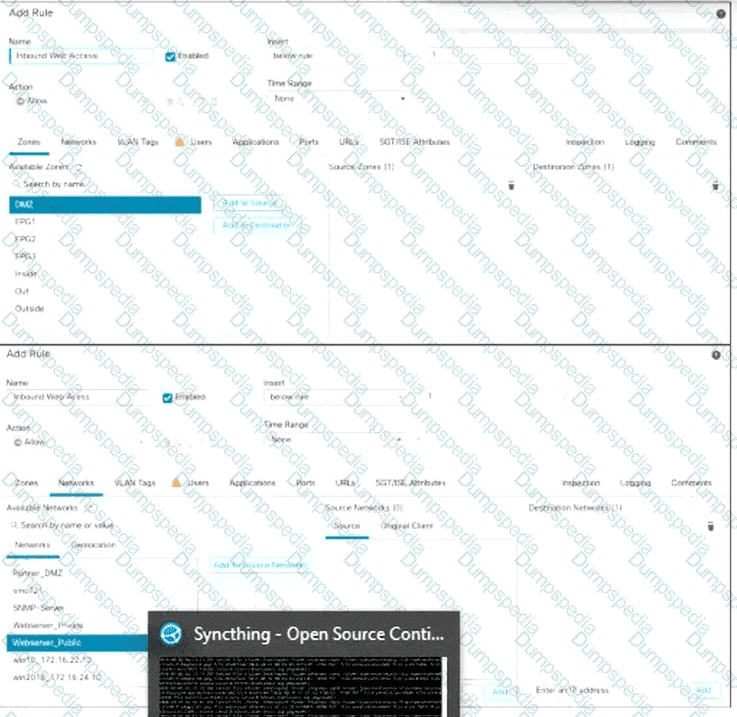
A security engineer is publishing a public web server located in the DMZ of a Cisco Secure Firewall Threat Defense device managed by Cisco Secure Firewall Management Center. The required network objects, Webserver_Private and Webserver_Public, are already defined, and an Auto NAT static rule mapping the public address to the private DMZ address is in place. The web server must be reachable from any source on the Internet. The engineer must configure a new Access Control Rule within the existing Access Control Policy. Which two configuration actions must be performed to meet the requirements? (Choose two.)
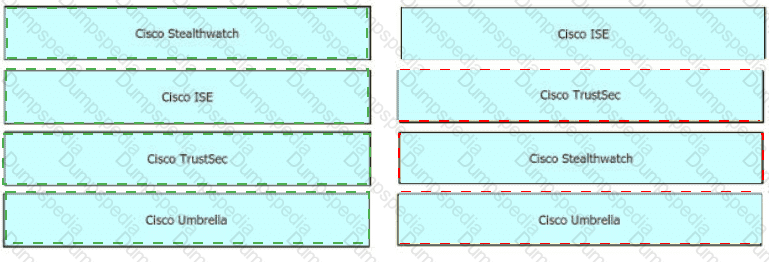
Which two products are used to forecast capacity needs accurately in real time? (Choose two.)
Which two types of policies are used by ZTNA to provide access to an application? (Choose two.)
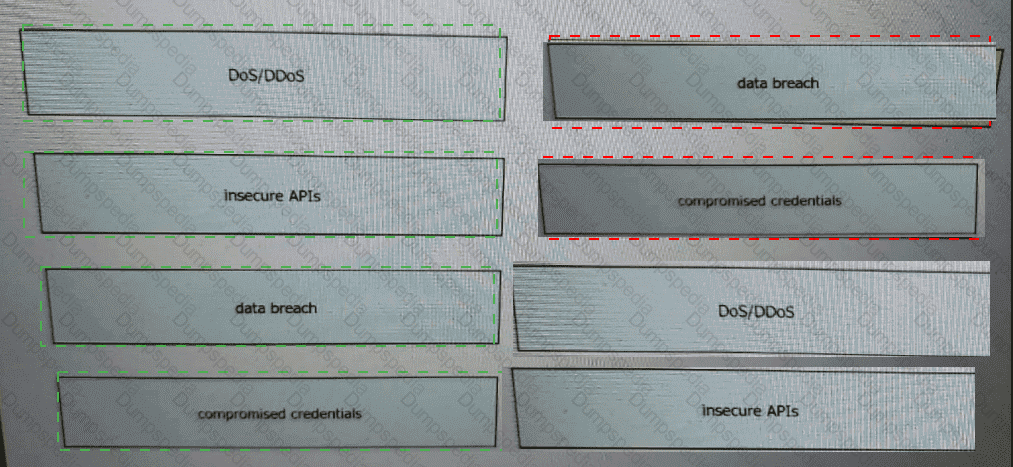
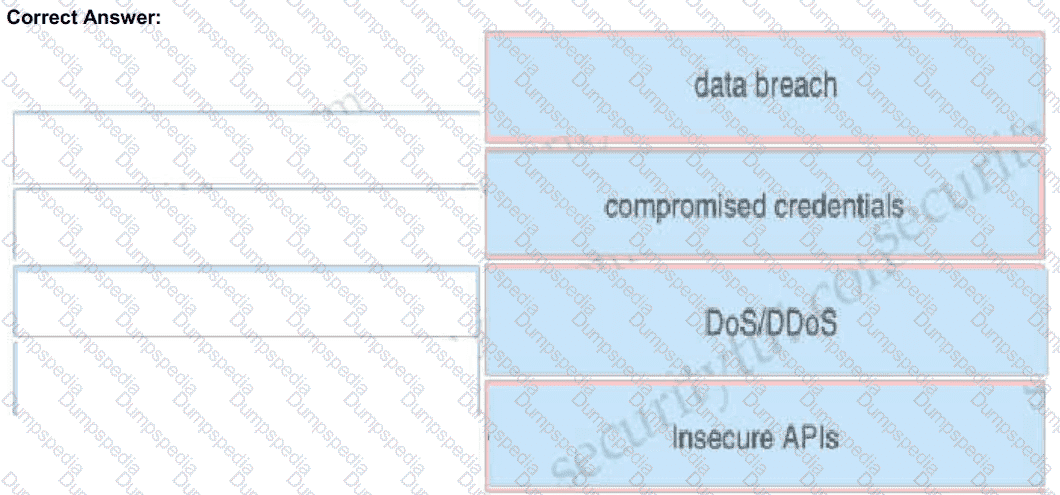
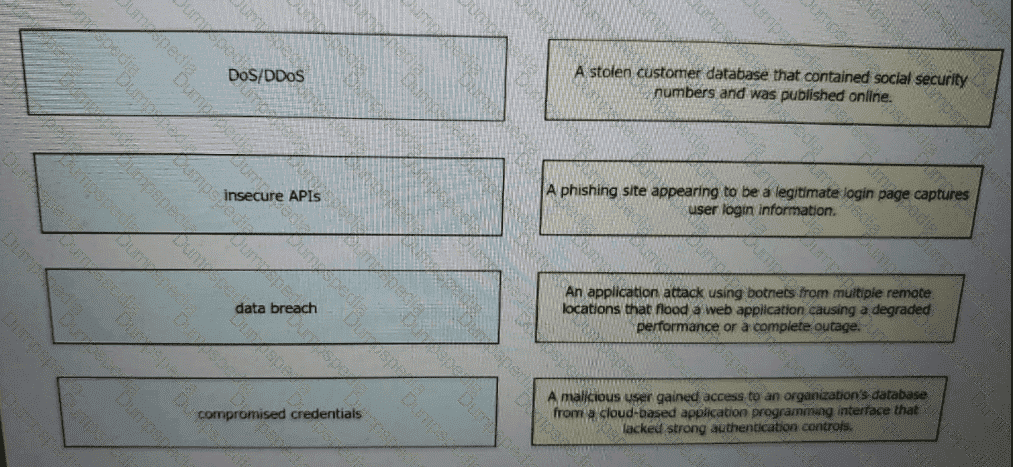
Drag and drop the threats from the left onto examples of that threat on the right
In a federated single sign-on environment, which protocol exchanges XML-based assertions between an identity provider and a service provider for authentication?
A security engineer must create a policy based on the reputation verdict of a file from a Cisco Secure Email Gateway. The file with an undetermined verdict must be dropped. Which action must the security engineer take to meet the requirement?
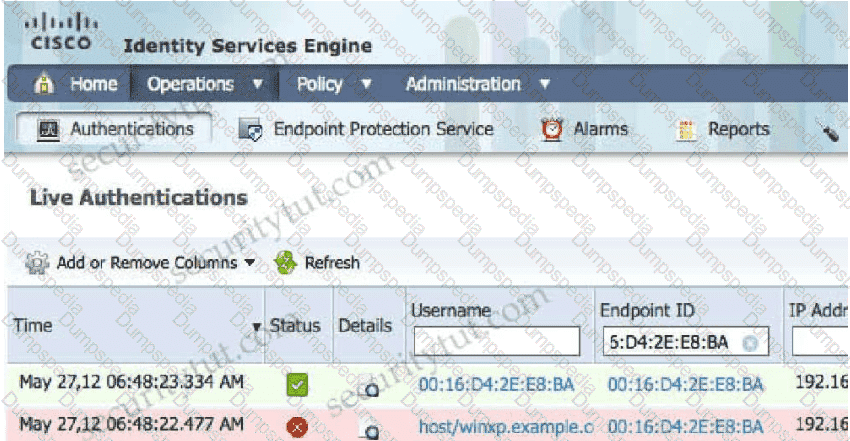
Which two configurations must be made on Cisco ISE and on Cisco TrustSec devices to force a session to be adjusted after a policy change is made? (Choose two)
Refer to the exhibit.
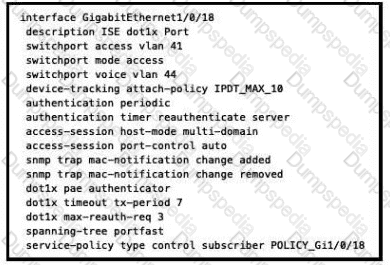
What will occur when this device tries to connect to the port?
An engineer needs to detect and quarantine a file named abc424400664 zip based on the MD5 signature of the file using the Outbreak Control list feature within Cisco Advanced Malware Protection (AMP) for Endpoints The configured detection method must work on files of unknown disposition Which Outbreak Control list must be configured to provide this?
Refer to the exhibit.
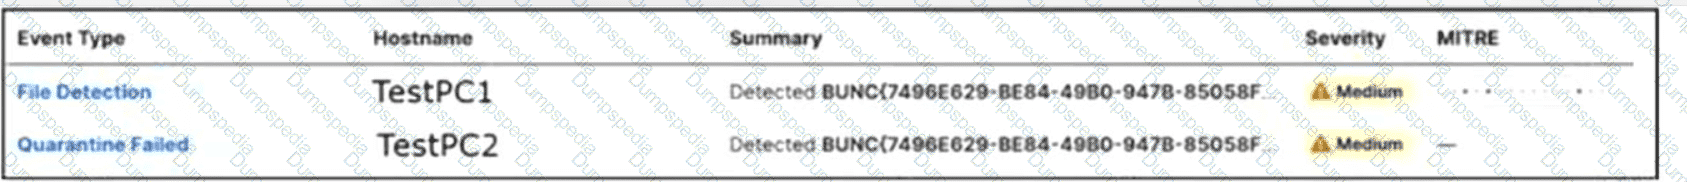
A Cisco Secure Endpoint malware event shows that a file was convicted as malicious and that its remediation status is Quarantine Failed. Before escalating the incident, the analyst must determine what can be concluded from the available event data. What is occurring based on the logs?
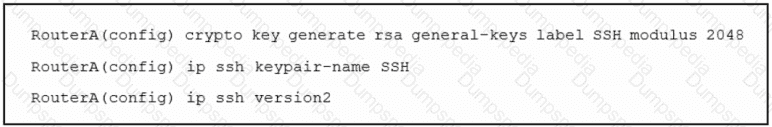
Refer to the exhibit. An engineer must enable secure SSH protocols and enters this configuration. What are two results of running this set of commands on a Cisco router? (Choose two.)
Which two components do southbound APIs use to communicate with downstream devices? (Choose two.)
Refer to the exhibit.
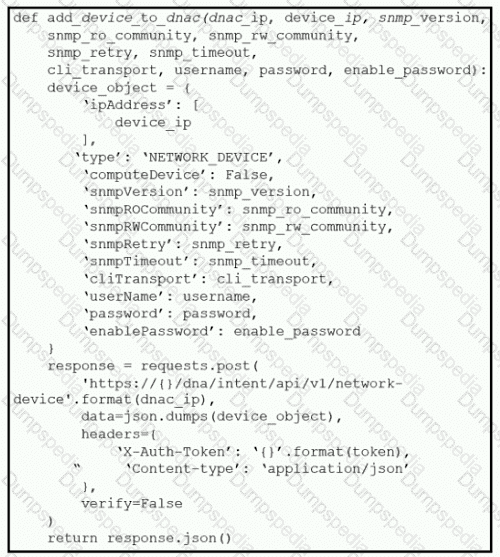
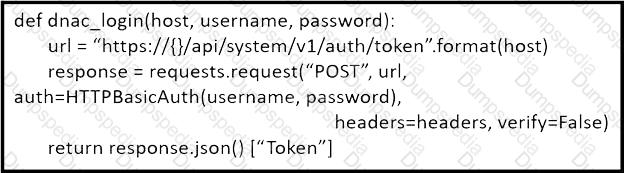
What is the result of this Python script of the Cisco DNA Center API?
An engineer enabled SSL decryption for Cisco Umbrella intelligent proxy and needs to ensure that traffic is inspected without alerting end-users.
Which Secure Email Gateway implementation method segregates inbound and outbound email?
An engineer has been tasked with configuring a Cisco FTD to analyze protocol fields and detect anomalies in the traffic from industrial systems. What must be done to meet these requirements?
Which feature enables a Cisco ISR to use the default bypass list automatically for web filtering?
Which cryptographic process provides origin confidentiality, integrity, and origin authentication for packets?
Which action must be taken in the AMP for Endpoints console to detect specific MD5 signatures on endpoints and then quarantine the files?
An organization has two systems in their DMZ that have an unencrypted link between them for communication.
The organization does not have a defined password policy and uses several default accounts on the systems.
The application used on those systems also have not gone through stringent code reviews. Which vulnerability
would help an attacker brute force their way into the systems?
When a Cisco Secure Web Appliance checks a web request, what occurs if it is unable to match a user-defined policy?
Which feature is leveraged by advanced antimalware capabilities to be an effective endpomt protection platform?
Which two statements about a Cisco WSA configured in Transparent mode are true? (Choose two)
Which technology provides the benefit of Layer 3 through Layer 7 innovative deep packet inspection,
enabling the platform to identify and output various applications within the network traffic flows?
Which policy is used to capture host information on the Cisco Firepower Next Generation Intrusion Prevention
System?
An organization is implementing URL blocking using Cisco Umbrella. The users are able to go to some sites
but other sites are not accessible due to an error. Why is the error occurring?
Cisco SensorBase gaihers threat information from a variety of Cisco products and services and performs analytics to find patterns on threats Which term describes this process?
Which Cisco Umbrella package supports selective proxy for Inspection of traffic from risky domains?
An engineer needs to add protection for data in transit and have headers in the email message Which configuration is needed to accomplish this goal?
Which exfiltration method does an attacker use to hide and encode data inside DNS requests and queries?
Refer to the exhibit.
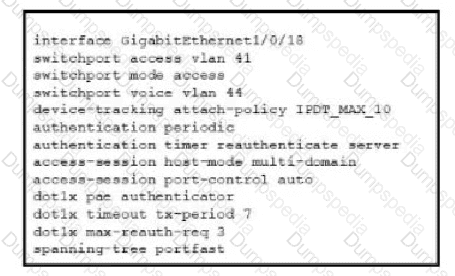
Refer to the exhibit. A Cisco ISE administrator adds a new switch to an 802.1X deployment and has difficulty with some endpoints gaining access.
Most PCs and IP phones can connect and authenticate using their machine certificate credentials. However printer and video cameras cannot base d on the interface configuration provided, what must be to get these devices on to the network using Cisco ISE for authentication and authorization while maintaining security controls?
A security engineer must add destinations into a destination list in Cisco Umbrella. What describes the application of these changes?
A network engineer must prevent endpoints from becoming infected by malicious files. The infrastructure includes Cisco Secure Endpoint, which must execute suspicious files in a cloud sandbox. Which feature must the engineer configure on Cisco Secure Endpoint to meet the requirement?
Which VMware platform does Cisco ACI integrate with to provide enhanced visibility, provide policy integration and deployment, and implement security policies with access lists?
Which mitigation strategy should be used to protect against session hijacking attacks in a cloud environment?
Which command is used to log all events to a destination colector 209.165.201.107?
Which method of attack is used by a hacker to send malicious code through a web application to an unsuspecting user to request that the victim ' s web browser executes the code?
A network administrator is configuring a switch to use Cisco ISE for 802.1X. An endpoint is failing
authentication and is unable to access the network. Where should the administrator begin troubleshooting to verify the authentication details?
An organization recently installed a Cisco Secure Web Appliance and would like to take advantage of the AVC engine to allow the organization to create a policy to control application-specific activity. After enabling the AVC engine, what must be done to implement this?
Which security control is required for identifying and neutralizing malicious code that attempts to execute on an endpoint?
A network engineer is deciding whether to use stateful or stateless failover when configuring two Cisco ASAs for high availability. What is the connection status in both cases?
A company has 5000 Windows users on its campus. Which two precautions should IT take to prevent WannaCry ransomware from spreading to all clients? (Choose two.)
An engineer is configuring Cisco Secure Endpoint to enhance network security by specifying a large set of external IP addresses that must be monitored for potential threats. The engineer is configuring an IP List and must add the IP addresses to the list. Which configuration action must the engineer take next to meet the requirement?
Which feature is used in a push model to allow for session identification, host reauthentication, and session termination?
A network administrator needs to find out what assets currently exist on the network. Third-party systems need to be able to feed host data into Cisco Firepower. What must be configured to accomplish this?
Which two actions does the Cisco identity Services Engine posture module provide that ensures endpoint security?(Choose two.)
What provides visibility and awareness into what is currently occurring on the network?
What must be configured on Cisco Secure Endpoint to create a custom detection tile list to detect and quarantine future files?
What is a functional difference between Cisco Secure Endpoint and Cisco Umbrella Roaming Client?
Which two characteristics of messenger protocols make data exfiltration difficult to detect and prevent?
(Choose two)
Which open standard underpins OpenID Connect, enabling Cisco Duo to authorize application access?
Which feature within Cisco ISE verifies the compliance of an endpoint before providing access to the
network?
Which feature is configured for managed devices in the device platform settings of the Firepower Management
Center?
With Cisco AMP for Endpoints, which option shows a list of all files that have been executed in your
environment?
Refer to the exhibit.
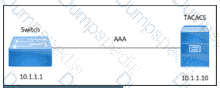
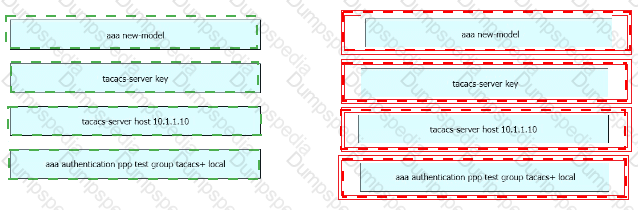
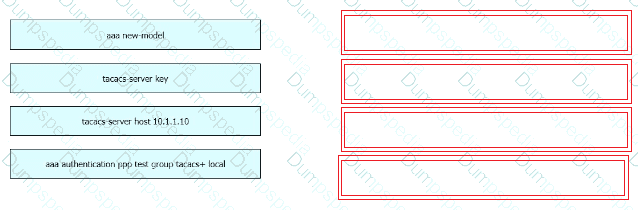
An engineer must configure a Cisco switch to perform PPP authentication via a TACACS server located at IP address 10.1.1.10. Authentication must fall back to the local database using the username LocalUser and password C1Sc0451069341l if the TACACS server is unreachable.
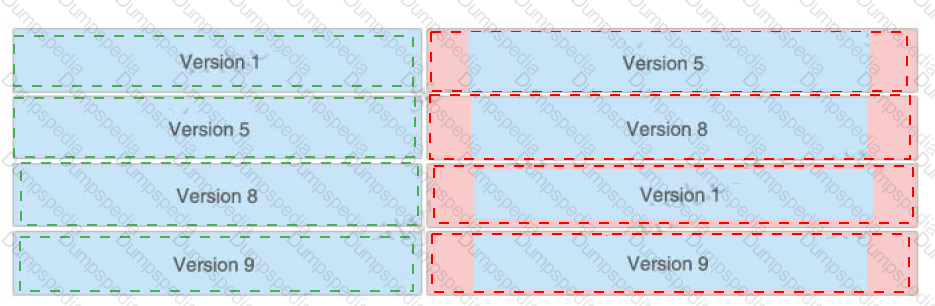
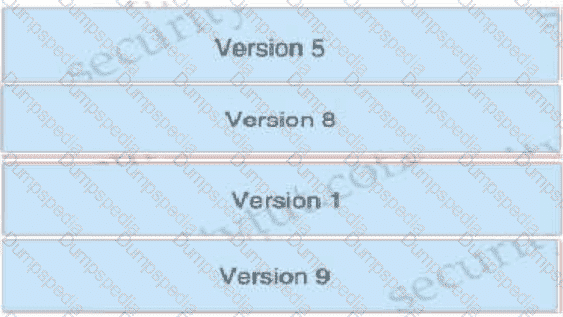
Drag and drop the commands from the left onto the corresponding configuration steps on the right.
An administrator is trying to determine which applications are being used in the network but does not want the
network devices to send metadata to Cisco Firepower. Which feature should be used to accomplish this?
An organization recently installed a Cisco WSA and would like to take advantage of the AVC engine to allow the organization to create a policy to control application specific activity. After enabling the AVC engine, what must be done to implement this?
How does Cisco Umbrella protect clients when they operate outside of the corporate network?
A network engineer must distribute an operating system image to a network device and activate the image on that device by using the Cisco Catalyst Center API. Which two API requests perform the required operations? (Choose two.)
A network engineer has been tasked with adding a new medical device to the network. Cisco ISE is being used as the NAC server, and the new device does not have a supplicant available. What must be done in order to securely connect this device to the network?
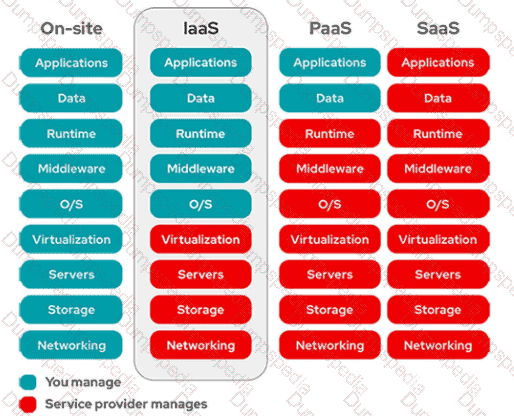
Which two aspects of the cloud PaaS model are managed by the customer but not the provider? (Choose two)
A network administrator is configuring a role in an access control policy to block certain URLs and selects the " Chat and instant Messaging " category. which reputation score should be selected to accomplish
this goal?
Which Cisco cloud security software centrally manages policies on multiple platforms such as Cisco ASA, Cisco Firepower, Cisco Meraki, and AWS?
An organization has a requirement to collect full metadata information about the traffic going through their AWS cloud services They want to use this information for behavior analytics and statistics Which two actions must be taken to implement this requirement? (Choose two.)
A network engineer is deciding whether to use stateful or stateless failover when configuring two ASAs for high availability. What is the connection status in both cases?
How many interfaces per bridge group does an ASA bridge group deployment support?
Which solution for remote workers enables protection, detection, and response on the endpoint against known and unknown threats?
An engineer is configuring Cisco WSA and needs to deploy it in transparent mode. Which configuration component must be used to accomplish this goal?
An engineer is configuring cloud logging on Cisco ASA and needs events to compress. Which component must be configured to accomplish this goal?
In which situation should an Endpoint Detection and Response solution be chosen versus an Endpoint Protection Platform?
A security engineer must protect endpoints when a file appears harmless during initial inspection but later shows malicious behavior. The solution must continuously observe process and file activity after execution and respond when a threat emerges. The infrastructure includes Cisco Secure Endpoint. Which feature must the engineer configure to meet the requirements?
What is the function of the crypto is a kmp key cisc406397954 address 0.0.0.0 0.0.0.0 command when establishing an IPsec VPN tunnel?
Which method is used to deploy certificates and configure the supplicant on mobile devices to gain access to
network resources?
A Cisco ESA network administrator has been tasked to use a newly installed service to help create policy based on the reputation verdict. During testing, it is discovered that the Cisco ESA is not dropping files that have an undetermined verdict. What is causing this issue?
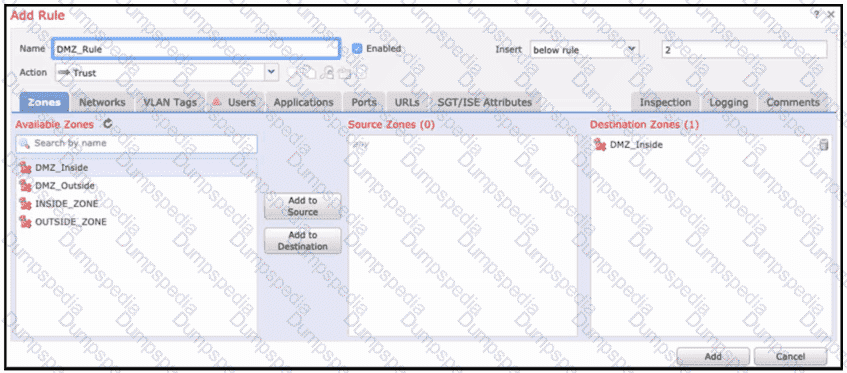
Refer to the exhibit. When configuring this access control rule in Cisco FMC, what happens with the traffic destined to the DMZ_inside zone once the configuration is deployed?
Which DevSecOps implementation process gives a weekly or daily update instead of monthly or quarterly in the applications?
A network engineer must enable SSH and SCP on a Cisco IOS router. The engineer has already generated the encryption keys and enabled SCP services on the router. Which configuration action must be performed next?
Which Cisco security solution integrates with cloud applications like Dropbox and Office 365 while protecting data from being exfiltrated?
An organization has DHCP servers set up to allocate IP addresses to clients on the LAN. What must be done to ensure the LAN switches prevent malicious DHCP traffic while also distributing IP addresses to the correct endpoints?
Which Cisco firewall solution supports configuration via Cisco Policy Language?
An engineer is configuring Cisco WSA and needs to enable a separated email transfer flow from the Internet and from the LAN. Which deployment mode must be used to accomplish this goal?
Refer to the exhibit.
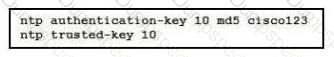
A network engineer is testing NTP authentication and realizes that any device synchronizes time with this router and that NTP authentication is not enforced What is the cause of this issue?
What are the two types of managed Intercloud Fabric deployment models? (Choose two.)
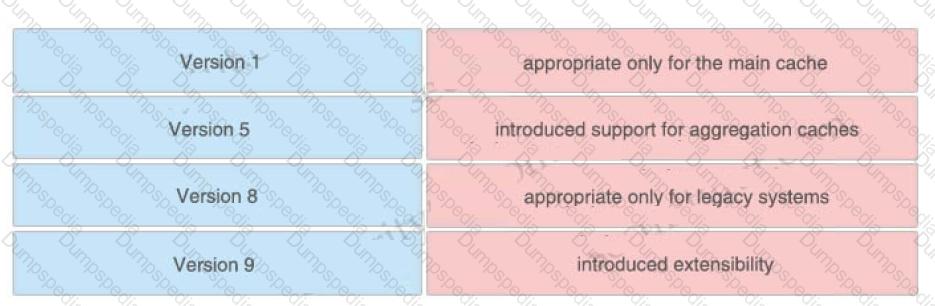
Drag and drop the NetFlow export formats from the left onto the descriptions on the right.
In which two ways does a system administrator send web traffic transparently to the Web Security Appliance?
(Choose two)
Which Cisco solution does Cisco Umbrella integrate with to determine if a URL is malicious?
An engineer wants to automatically assign endpoints that have a specific OUI into a new endpoint group. Which
probe must be enabled for this type of profiling to work?
Which type of API is being used when a security application notifies a controller within a software-defined network architecture about a specific security threat?
Based on the NIST 800-145 guide, which cloud architecture may be owned, managed, and operated by one or more of the organizations in the community, a third party, or some combination of them, and it may exist on or off premises?
Which Cisco ISE service checks the compliance of endpoints before allowing the endpoints to connect to
the network?
Which action configures the IEEE 802.1X Flexible Authentication feature lo support Layer 3 authentication mechanisms?
Which two preventive measures are used to control cross-site scripting? (Choose two)
An administrator is establishing a new site-to-site VPN connection on a Cisco IOS router. The organization
needs to ensure that the ISAKMP key on the hub is used only for terminating traffic from the IP address of
172.19.20.24. Which command on the hub will allow the administrator to accomplish this?
A security engineer is deploying an IPsec site-to-site VPN between headquarters and a remote plant, protected by Cisco Secure Firewall Threat Defense managed by Cisco Secure Firewall Management Center. The following configurations have already been completed:
Matching IKEv2 proposals, preshared keys, and IPsec transform sets
Access control rules permitting the traffic
Crypto maps applied to the outside interfaces
VPN traffic exempted from inspection
During a packet capture on the firewall, the engineer observes that the traffic is translated to the public IP address, preventing tunnel establishment. Which configuration action must be performed next?
Which feature of a secure CI/CD pipeline defends container workloads against detected exploits, application flaws, configuration errors, and policy violations?
Which method must be used to connect Cisco Secure Workload to external orchestrators at a client site when the client does not allow incoming connections?
Refer to the exhibit.
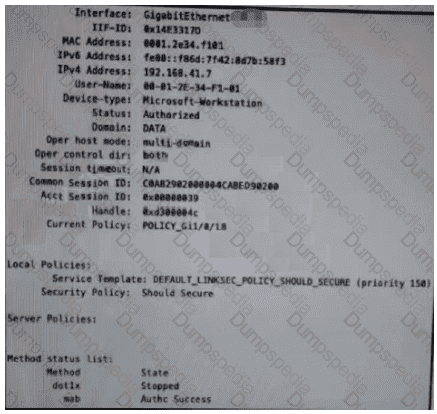
Which configuration item makes it possible to have the AAA session on the network?
A Cisco FTD engineer is creating a new IKEv2 policy called s2s00123456789 for their organization to allow for additional protocols to terminate network devices with. They currently only have one policy established and need the new policy to be a backup in case some devices cannot support the stronger algorithms listed in the primary policy. What should be done in order to support this?
Which technology should be used to help prevent an attacker from stealing usernames and passwords of users within an organization?
Which two application layer preprocessors are used by Firepower Next Generation Intrusion Prevention
System? (Choose two)
Which two capabilities of Integration APIs are utilized with Cisco DNA center? (Choose two)
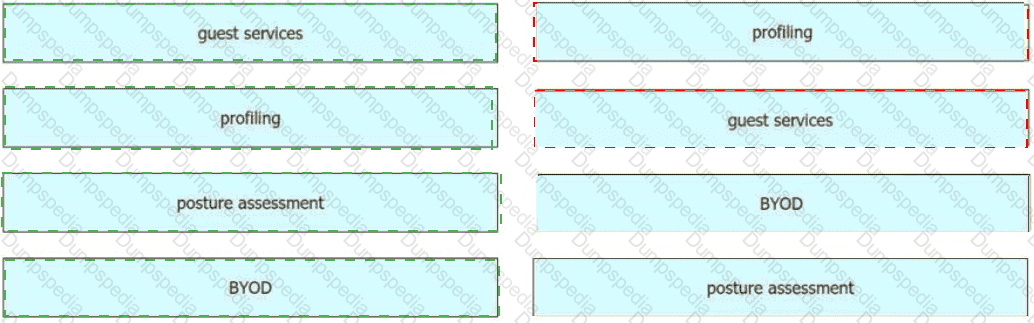
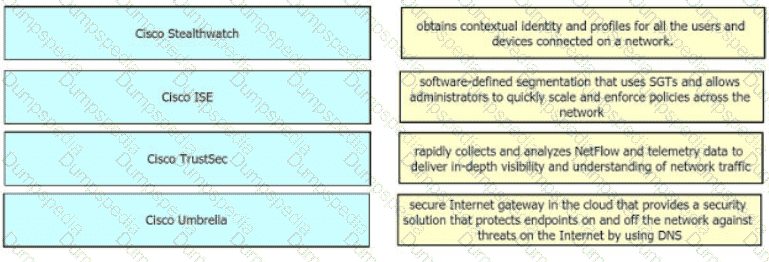
Drag and drop the solutions from the left onto the solution ' s benefits on the right.
An engineer is deploying a Cisco Secure Email Gateway and must ensure it reaches the Cisco update servers to retrieve new rules. The engineer must now manually configure the Outbreak Filter rules on an AsyncOS for Cisco Secure Email Gateway. Only outdated rules must be replaced. Up-to-date rules must be retained. Which action must the engineer take next to complete the configuration?
Which technology limits communication between nodes on the same network segment to individual applications?
Which algorithm provides encryption and authentication for data plane communication?
Which solution protects hybrid cloud deployment workloads with application visibility and segmentation?
For a given policy in Cisco Umbrella, how should a customer block websites based on a custom list?
A mall provides security services to customers with a shared appliance. The mall wants separation of
management on the shared appliance. Which ASA deployment mode meets these needs?
What are two functionalities of northbound and southbound APIs within Cisco SDN architecture? (Choose two.)
A Cisco Firepower administrator needs to configure a rule to allow a new application that has never been seen
on the network. Which two actions should be selected to allow the traffic to pass without inspection? (Choose
two)
Which cloud service model offers an environment for cloud consumers to develop and deploy applications
without needing to manage or maintain the underlying cloud infrastructure?
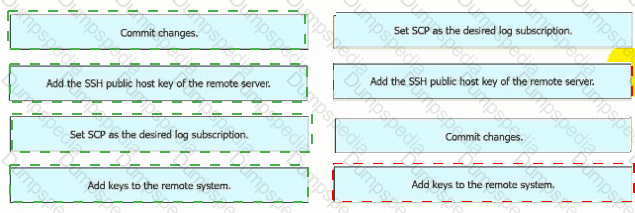
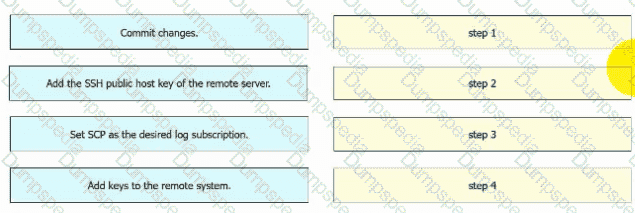
An engineer must configure AsyncOS for Cisco Secure Web Appliance to push log files to a syslog server using the SCP retrieval method. Drag and drop the steps from the left into the sequence on the right to complete the configuration.
Which Cisco IOS XE command rejects packets with a source IP address that fails a reverse-path-forwarding prefix check on the ingress interface?
Why is it important to have logical security controls on endpoints even though the users are trained to spot security threats and the network devices already help prevent them?
An engineer configured a new network identity in Cisco Umbrella but must verify that traffic is being routed
through the Cisco Umbrella network. Which action tests the routing?
Which parameter is required when configuring a Netflow exporter on a Cisco Router?
Which Talos reputation center allows you to track the reputation of IP addresses for email and web traffic?
A network engineer entered the snmp-server user asmith myv7 auth sha cisco priv aes 256
cisc0xxxxxxxxx command and needs to send SNMP information to a host at 10.255.255.1. Which
command achieves this goal?
What is a benefit of using Cisco AVC (Application Visibility and Control) for application control?
Which capability is exclusive to a Cisco AMP public cloud instance as compared to a private cloud instance?
What is a benefit of a Cisco Secure Email Gateway Virtual as compared to a physical Secure Email Gateway?
An organization uses Cisco FMC to centrally manage multiple Cisco FTD devices The default management port conflicts with other communications on the network and must be changed What must be done to ensure that all devices can communicate together?
What are the components of endpoint protection against social engineering attacks?
An organization is using DNS services for their network and want to help improve the security of the DNS infrastructure. Which action accomplishes this task?
An organization must add new firewalls to its infrastructure and wants to use Cisco ASA or Cisco FTD.
The chosen firewalls must provide methods of blocking traffic that include offering the user the option to bypass the block for certain sites after displaying a warning page and to reset the connection. Which solution should the organization choose?
Which term describes when the Cisco Firepower downloads threat intelligence updates from Cisco Talos?
In which type of attack does the attacker insert their machine between two hosts that are communicating with each other?
A security engineer is deploying an IPsec site-to-site VPN between headquarters and a remote plant, protected by Cisco Secure Firewall Threat Defense managed by Cisco Secure Firewall Management Center. The following configurations have already been completed:
Matching IKEv2 proposals, preshared keys, and IPsec transform sets
Access control rules permitting the traffic
Crypto maps applied to the outside interfaces
VPN traffic exempted from inspection
During a packet capture on the firewall, the engineer observes that the traffic is translated to the public IP address, preventing tunnel establishment. Which configuration action must be performed next?
An engineer notices traffic interruption on the network. Upon further investigation, it is learned that broadcast
packets have been flooding the network. What must be configured, based on a predefined threshold, to
address this issue?
Which protocol provides the strongest throughput performance when using Cisco AnyConnect VPN?
Which two request methods of REST API are valid on the Cisco ASA Platform? (Choose two.)
Which solution offers automated blocking of known threats and visibility into zero-day attack behavior, with the ability to respond directly from the console?
An engineer is deploying a Cisco Secure Email Gateway and must configure a sender group that decides which mail policy will process the mail. The configuration must accept incoming mails and relay the outgoing mails from the internal server. Which component must be configured to accept the connection to the listener and meet these requirements on a Cisco Secure Email Gateway?
An engineer is configuring 802.1X authentication on Cisco switches in the network and is using CoA as a mechanism. Which port on the firewall must be opened to allow the CoA traffic to traverse the network?
A malicious user gained network access by spoofing printer connections that were authorized using MAB on
four different switch ports at the same time. What two catalyst switch security features will prevent further
violations? (Choose two)
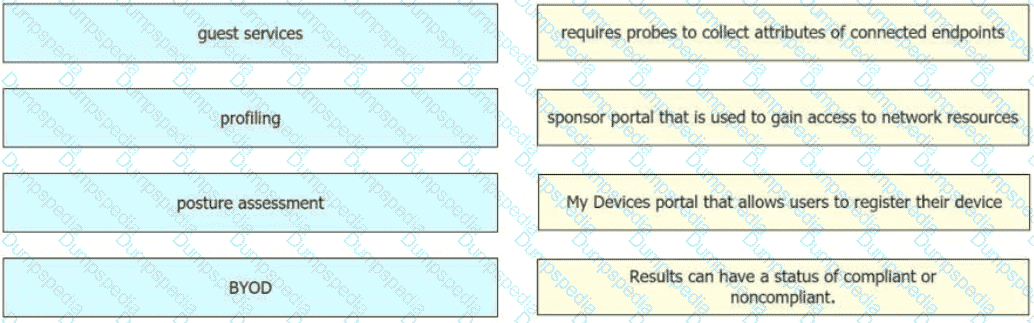
Drag and drop the concepts from the left onto the correct descriptions on the right
What is a language format designed to exchange threat intelligence that can be transported over the TAXII
protocol?
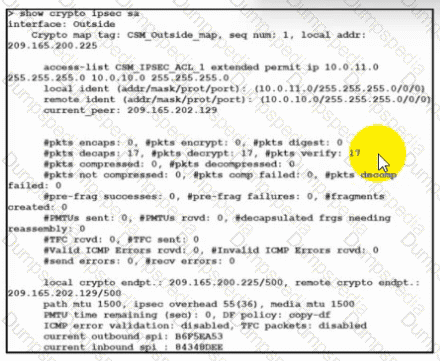
Refer to the exhibit. Traffic is not passing through IPsec site-to-site VPN on the Secure Firewall Threat Defense appliance. What is causing this issue?
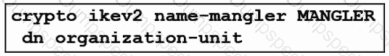
Refer to the exhibit. An engineer is implementing a certificate-based VPN. What is the result of the existing configuration?
How does Cisco Workload Optimization portion of the network do EPP solutions solely performance issues?
Which Cisco security solution secures public, private, hybrid, and community clouds?
Which functions of an SDN architecture require southbound APIs to enable communication?
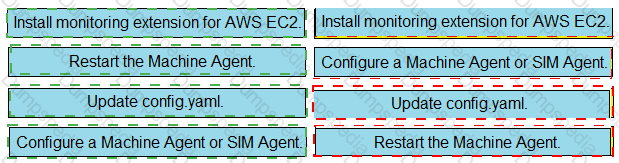
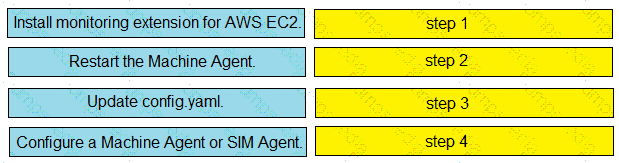
Drag and drop the steps from the left into the correct order on the right to enable AppDynamics to monitor an EC2 instance in Amazon Web Services.
A large retail enterprise is deploying Cisco Secure Private Access to enable remote employees to reach internal applications without manual intervention. The IT department requires a seamless, zero-touch enrollment process in which users are registered and authenticated transparently without requiring end-user action. The architecture must support robust high availability for back-end connectivity to ensure continuous access to private resources. Which configuration approach must the administrator implement to meet the requirement?
A large enterprise is currently managing a hybrid environment consisting of a private data center and multiple public cloud providers. The security engineering team is concerned about “Shadow IT” and the lack of visibility into unauthorized cloud services being used by various departments. The architect must select a solution that provides comprehensive discovery of cloud application usage and assesses the risk of each service based on industry certifications. Which technical solution must be used to provide cross-environment visibility?
A Cisco Secure Email Gateway network administrator has been tasked to use a newly installed service to help create policy based on the reputation verdict. During testing, it is discovered that the Secure Email Gateway is not dropping files that have an undetermined verdict. What is causing this issue?
An engineer is configuring their router to send NetfFow data to Stealthwatch which has an IP address of 1 1 11 using the flow record Stea!thwatch406397954 command Which additional command is required to complete the flow record?
Refer to the exhibit.
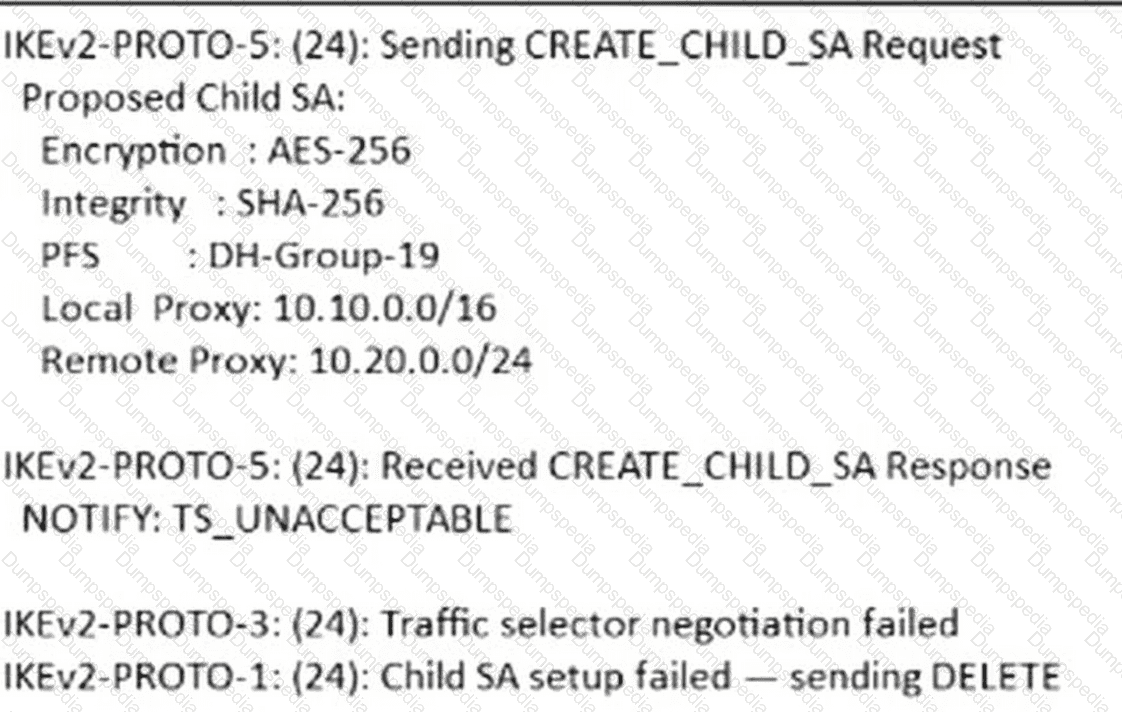
A site-to-site IKEv2 VPN between two Cisco Secure Firewall Threat Defense devices at a healthcare organization completes IKE Phase 1 successfully but fails during CREATE_CHILD_SA. The engineer captures the debug output from the initiating Cisco Secure Firewall. Which action must be performed to resolve the issue?
A network administrator is using the Cisco ESA with AMP to upload files to the cloud for analysis. The network
is congested and is affecting communication. How will the Cisco ESA handle any files which need analysis?
Which public cloud provider supports the Cisco Next Generation Firewall Virtual?
A network engineer is enabling RADIUS CoA on a fleet of Cisco Catalyst switches so that Cisco ISE can quarantine compromised endpoints in real time. To uniquely target an active session for disconnect or reauthorization, Cisco ISE must include IETF attribute 31 to identify the endpoint. Which configuration action must be performed on Cisco ISE to meet the requirement?
Which product allows Cisco FMC to push security intelligence observable to its sensors from other products?
What provides total management for mobile and PC including managing inventory and device tracking, remote view, and live troubleshooting using the included native remote desktop support?
A Cisco ESA administrator has been tasked with configuring the Cisco ESA to ensure there are no viruses before quarantined emails are delivered. In addition, delivery of mail from known bad mail servers must be prevented. Which two actions must be taken in order to meet these requirements? (Choose two)
A small organization needs to reduce the VPN bandwidth load on their headend Cisco ASA in order to
ensure that bandwidth is available for VPN users needing access to corporate resources on the10.0.0.0/24 local HQ network. How is this accomplished without adding additional devices to the
network?
Which Cisco DNA Center Intent API action is used to retrieve the number of devices known to a DNA Center?
A security engineer is tasked with configuring TACACS on a Cisco ASA firewall. The engineer must be able to access the firewall command line interface remotely. The authentication must fall back to the local user database of the Cisco ASA firewall. AAA server group named TACACS-GROUP is already configured with TACACS server IP address 192.168.10.10 and key C1sc0512222832!. Which configuration must be done next to meet the requirement?
An attacker needs to perform reconnaissance on a target system to help gain access to it. The system has weak passwords, no encryption on the VPN links, and software bugs on the system’s applications. Which
vulnerability allows the attacker to see the passwords being transmitted in clear text?
Which suspicious pattern enables the Cisco Tetration platform to learn the normal behavior of users?
Which Cisco platform onboards the endpoint and can issue a CA signed certificate while also automatically configuring endpoint network settings to use the signed endpoint certificate, allowing the endpoint to gain network access?
A financial services firm is concerned about employees inadvertently pasting sensitive customer account information into public generative AI websites. The security team needs to implement a solution that inspects outbound traffic and prevents the transmission of sensitive data to AI platforms. Which two configuration actions must the administrator perform on Cisco Secure Access to achieve the requirement? (Choose two.)
Which two services are provided by the Cisco Talos Incident Response group? (Choose two.)
Which OWASP LLM risk involves an attacker embedding hidden instructions in user input to manipulate the model’s behavior?
Which network monitoring solution uses streams and pushes operational data to provide a near real-time view
of activity?
Which two global commands must the network administrator implement to limit the attack surface of an internet-facing Cisco router? (Choose two.)
Which two are valid suppression types on a Cisco Next Generation Intrusion Prevention System? (Choose two)
Which Cisco ASA deployment model is used to filter traffic between hosts in the same IP subnet using higher-level protocols without readdressing the network?
Which two features are used to configure Cisco ESA with a multilayer approach to fight viruses and malware?
(Choose two)
Which VPN technology can support a multivendor environment and secure traffic between sites?
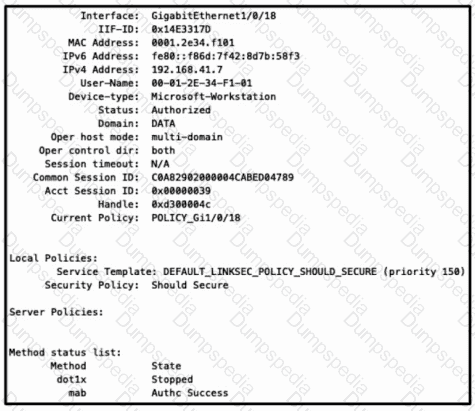
Refer to the exhibit. Which configuration item makes it possible to have the AAA session on the network?
Refer to the exhibit.
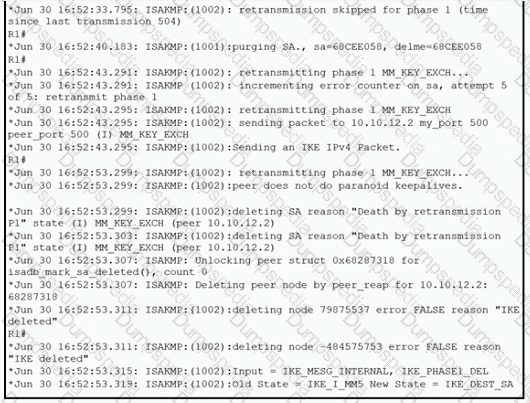
A network administrator configured a site-to-site VPN tunnel between two Cisco IOS routers, and hosts are unable to communicate between two sites of VPN. The network administrator runs the debug crypto isakmp sa command to track VPN status. What is the problem according to this command output?
What is the process of performing automated static and dynamic analysis of files against preloaded
behavioral indicators for threat analysis?
An engineer recently completed the system setup on a Cisco WSA Which URL information does the system send to SensorBase Network servers?
A healthcare organization is deploying Cisco Secure Access to prevent protected health information from being shared with generative AI services. The security team requires real-time DLP inspection only for traffic destined for AI applications, with minimal false positives during general web browsing. The policy must permit tuning based on the proximity and match counts of PHI identifiers. Which configuration action must the engineer perform?
An engineer implements Cisco CloudLock to secure a Microsoft Office 365 application in the cloud. The engineer must configure protection for corporate files in case of any incidents. Which two actions must be taken to complete the implementation? (Choose two.)
Refer to the exhibit.
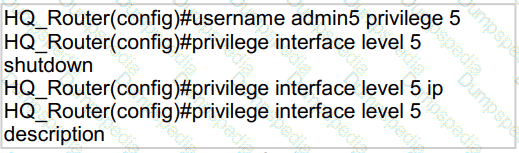
A network administrator configures command authorization for the admin5 user. What is the admin5 user able to do on HQ_Router after this configuration?
Which two functions does the Cisco Advanced Phishing Protection solution perform in trying to protect from phishing attacks? (Choose two.)
An organization wants to improve its cybersecurity processes and to add intelligence to its data The organization wants to utilize the most current intelligence data for URL filtering, reputations, and vulnerability information that can be integrated with the Cisco FTD and Cisco WSA What must be done to accomplish these objectives?
TESTED 14 Oct 2026