dumpspedia logo
A security operations center analyst is using the command line to display specific traffic.
The analyst uses the following command:
$tshark -r file.pcap -Y "http or udp"
Which of the following will the command line display?
A security analyst isolates a Windows 11 workstation from the network after known malware is detected. The list of security information and event management (SIEM) events during the malware installation and timeline does not identify a specific user who was logged in. The security analyst uses the local administrative account to log in and would like a list of logins to the machine.
Which of the following PowerShell commands should the analyst use?
A security team reviews a penetration testing report of a web application that contains multiple cross-site scripting (XSS) and Structured Query Language injection (SQLi) vulnerabilities.
Which of the following is most likely causing these to occur?
An analyst reviews the following system logs from a recent breach attempt:
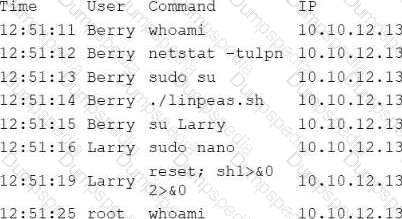
Which of the following techniques did the attacker attempt to use?
Which of the following contains stakeholder contact information for incident response reporting?
A cybersecurity analyst receives an unstructured text document that contains advanced persistent threat (APT)-related indicators of compromise (IoCs). The analyst needs to extract the IPv4 addresses.
Which of the following is the best tool to accomplish this task?
Which of the following phases of the incident response process will permanently remove an attacker’s access to corporate resources?
The Chief Information Officer (CIO) is requiring users to phase out a legacy system that no longer receives security updates because the system will be decommissioned soon.
Which of the following risk management strategies is the CIO using?
Before merging with a software company, the acquiring company's legal team requires a detailed software scan to determine if all code base is using open-source or paid licensed libraries. The vulnerability management analyst needs to provide this report.
Which of the following scan methods will best meet this requirement?
An analyst receives the following output:
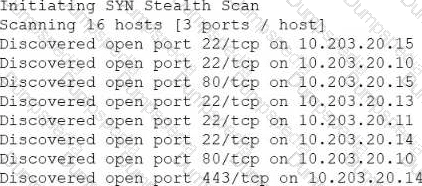
Which of the following is the correct number of discovered systems that are allowing unencrypted traffic?
A security analyst responds to an alert regarding identity and access management activity within the cloud environment. The attacker is currently trying to gain access from one isolated cloud subscription to another via a compromised user role.
Which of the following aspects of the MITRE ATT & CK framework is the attacker trying to perform?
The Chief Information Security Officer (CISO) reviews the following security operations metrics from the last month:
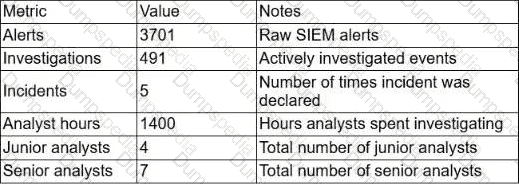
Which of the following is the best action to improve overall security operations efficiency?
Which of the following is the most important reason why tactics, techniques, and procedures (TTP) are beneficial to a defensive strategy?
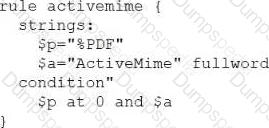
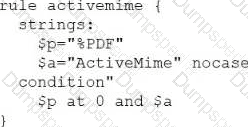
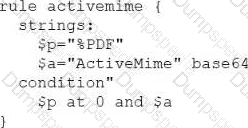
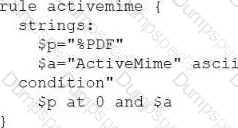
A security analyst must identify documents that contain encoded ActiveMime payloads in a directory containing thousands of files. The analyst runs the following command: grep -rail ActiveMime *
The command returns no output.
Which of the following Yet Another Recursive Acronym (YARA) rules should the analyst use to find the suspicious files?
A)
B)
C)
D)
An analyst executes the top command on a Linux system for an unresponsive application and observes the following output:
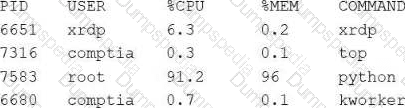
Which of the following is the most likely cause of this issue?
Which of the following best describes a type of risk that exists after mitigations or controls are enacted and implemented?
A vulnerability analyst runs a credentialed vulnerability scan covering all addressable enterprise assets. After running the scan, the analyst discovers a large number of critical vulnerabilities that cannot be immediately remediated.
Which of the following are the most likely reasons why the vulnerabilities cannot be immediately addressed?
Which of the following is the most comprehensive type of report associated with a closed incident?
An analyst performs Nmap scans to determine which hosts may need to be targeted to deploy a critical Windows patch. The patch for the vulnerability is to address a critical security flaw that targets open Server Message Block (SMB) ports on Windows systems only.
The analyst scans with the following command:
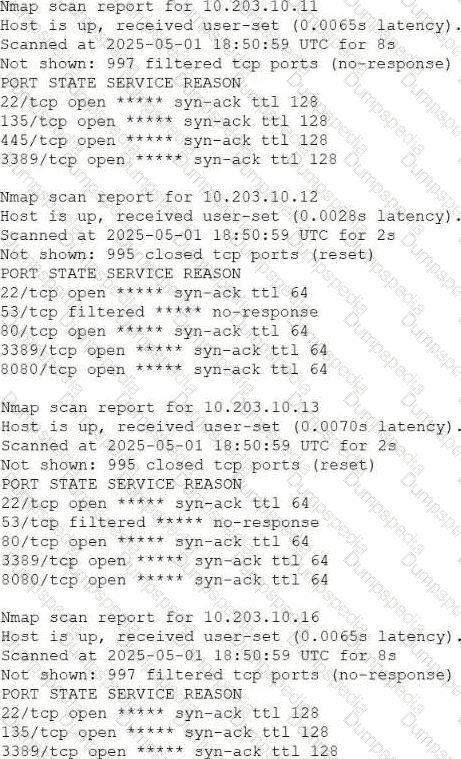
$sudo nmap -Pn 10.203.10.0/24
The analyst then receives the following output:
Which of the following hosts should the analyst prioritize for patching?
A security operations center (SOC) manager reviews a document signed by the Chief Financial Officer (CFO), the sales director, and a customer to decide whether a contract breach occurred.
Which of the following best describes the document that includes key performance indicators (KPIs)?
Which of the following is the most likely reason an organization might implement compensating controls?
TESTED 21 Sep 2026