Month End Sale - Limited Time 70% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: 70xmasdy

Welcome To DumpsPedia

NSE5_FSW_AD-7.6 Sample Questions Answers

Questions 4

Refer to the exhibit.

4

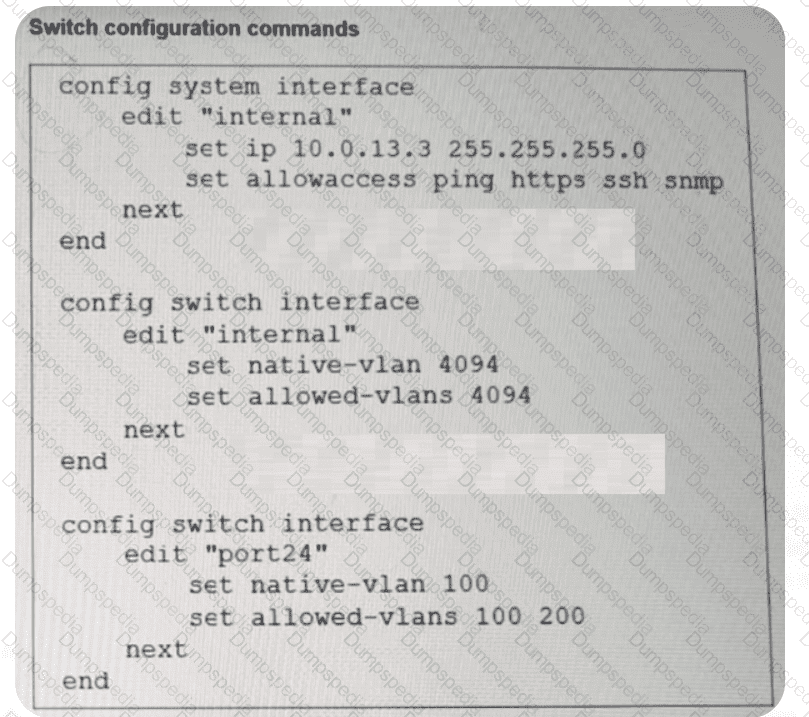
Port24 is the only uplink port connected to the network where you need access to FortiSwitch management services. However, FortiSwitch is not accessible on its management interface with IP address 10.0.13.3. Based on the configuration shown in the exhibit, which two actions should you take to fix the issue and access FortiSwitch? (Choose two answers)

Options:

A.

Change the management IP address to use the VLAN 100 subnet.

B.

Change the native VLAN on port24 to VLAN 4094.

C.

Remove VLAN 200 from the allowed VLANs on port24.

D.

Add VLAN 4094 to the allowed VLANs on port24.

Buy Now
Questions 5

Exhibit.

port24 is the only uplink port connected to the network where access to FortiSwitch management services is possible. However, FortiSwitch is still not accessible on the management interface. Which two actions should you take to fix the issue and access FortiSwitch? (Choose two.)

Options:

A.

You must add port24 native VLAN as an allowed VLAN on internal.

B.

You must add VLAN ID 200 to the allowed VLANS on internal.

C.

You must allow VLAN ID 4094 on port24, if management traffic is tagged.

D.

You should use VLAN ID 4094 as the native VLAN on port24.

Buy Now
Questions 6

(Full question statement start from here)

You are deploying a FortiSwitch virtual stack in a network that contains Cisco devices. You want the Cisco devices toautomatically discover the FortiSwitch devices and exchange device information. Which two protocols must be enabled on the FortiSwitch devices to achieve this? (Choose two answers)

Options:

A.

Unidirectional Link Detection

B.

Cisco Discovery Protocol

C.

Link Layer Discovery Protocol

D.

LLDP – Media Endpoint Discovery

Buy Now
Questions 7

Refer to the exhibit.

7

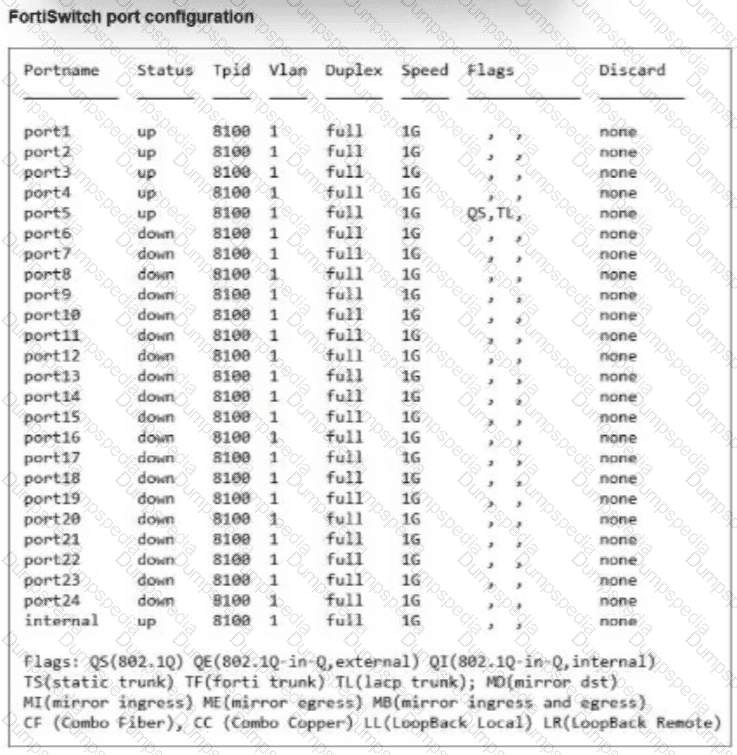
You run the command diagnose switch physical-ports summary on FortiSwitch.

Based on exhibit, what does the output indicate to about the FortiSwitch mode? (Choose one answer)

Options:

A.

FortiSwitch is configured as access ports.

B.

FortiSwitch is configured as a layer 3 router.

C.

FortiSwitch is in standalone mode.

D.

FortiSwitch is operating in managed mode.

Buy Now
Questions 8

Which two rules used by MSTP are similar to rules used by other STP methods? (Choose two.)

Options:

A.

MSTP uses port role election, similar to rapid STP on the instances.

B.

MSTP uses alternate path and primary path, similar to regular STP.

C.

MSTP uses root bridge selection, similar to rapid STP

D.

MSTP uses timers for transitioning the ports, similar to regular STP.

Buy Now
Questions 9

Exhibit.

9

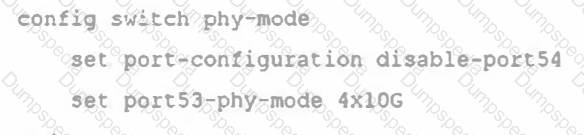
What conditions does a FortiSwitch need to have to successfully configure the options shown in the exhibit above? (Choose two.)

Options:

A.

The FortiSwitch model is equipped with a maximum of 54 interfaces.

B.

The CLI commands are enabling a splitpo rt into four 10Gbps interfaces.

C.

The port full speed prior the split was 100G SFP+

D.

The split port can be assigned to native VLAN

Buy Now
Questions 10

Which statement about 802.1X security profiles using MAC-based authentication mode is true?

Options:

A.

FortiSwitch allows connectivity to all hosts connected to a port, if one host is authenticated.

B.

FortiSwitch can grant each device a different access level based on the credentials provided

C.

FortiSwitch performs faster when using this security mode on the ports.

D.

FortiSwitch must communicate with the RADIUS server to authenticate devices

Buy Now
Questions 11

Refer to the exhibit.

11

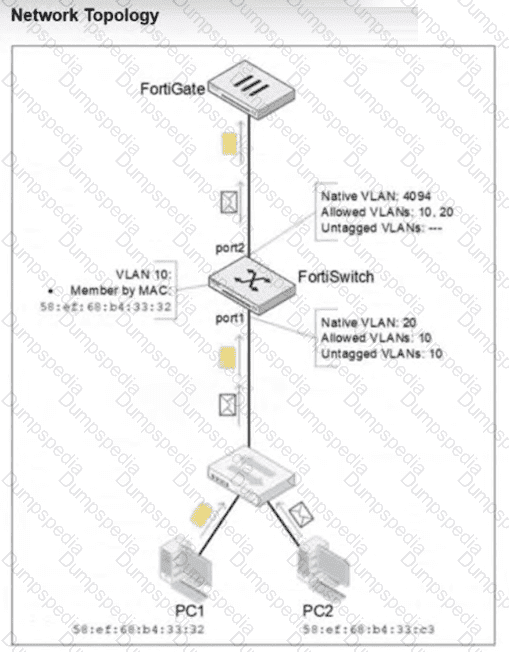
PC1 and PC2 are connected to port1 on FortiSwitch. Which VLAN tags will FortiSwitch apply when forwarding PC1 and PC2 traffic out of port2? (Choose one answer)

Options:

A.

FortiSwitch will tag PC1 and PC2 frames with VLAN 20.

B.

FortiSwitch will tag both PC1 and PC2 frames with VLAN 10, due to MAC override.

C.

FortiSwitch will tag PC1 frames with VLAN 10 and PC2 frames with VLAN 20.

D.

FortiSwitch will leave PC1 frames untagged and will tag PC2 frames with VLAN 10.

Buy Now
Questions 12

Refer to the exhibits.

12

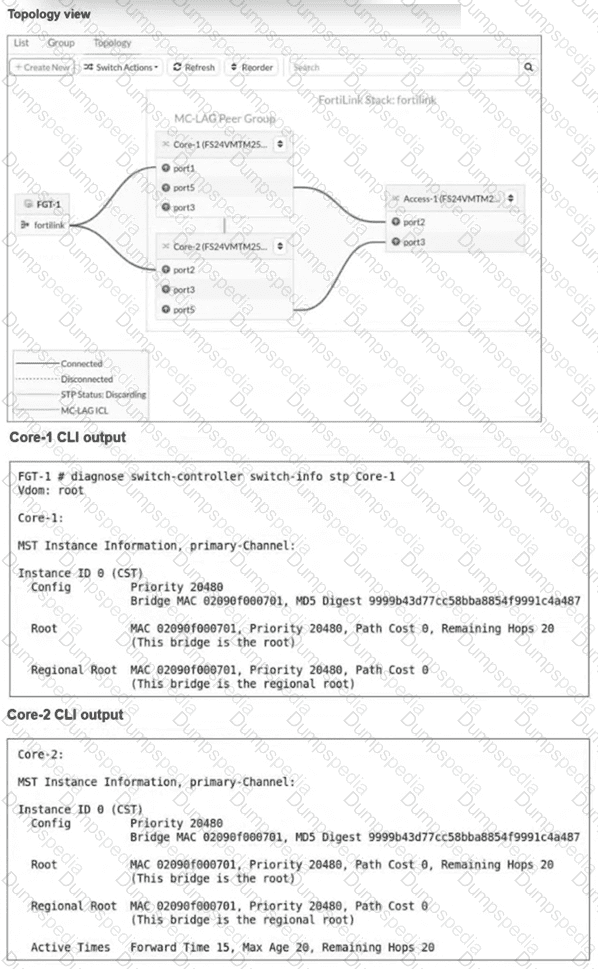
An administrator has deployed two FortiSwitch devices, Core-1 and Core-2, as multichassis link aggregation group (MCLAG) peers. These switches are connected to FortiGate for FortiLink and to an access switch (Access-1) using an inter-switch link (ISL). After configuration, the administrator notices that both Core-1 and Core-2 are claiming to be the root bridge in the Multiple Spanning Tree Protocol (MSTP) topology. What explains this behavior? (Choose one answer)

Options:

A.

FortiGate participates in MSTP and causes both switches to assume the root bridge role.

B.

The ISL was not configured correctly, leading to MSTP inconsistency.

C.

Both switches share the same bridge ID because MCLAG treats them as one logical switch.

D.

MCLAG automatically disables STP on all peer switches.

Buy Now
Questions 13

An administrator needs to deploy managed FortiSwitch devices in a remote location where multiple VLANs must be utilized to segment devices. No Layer 3 switch or router is present. The the only WAN connectivity is the router provided by the ISP connected to the public internet.

Which two items will the administrator need to use? (Choose two.)

Options:

A.

A FortiSwitch interface connected to the ISP router configured with fortilink-13-mode enabled.

B.

FortiSwitch and FortiGate devices configured with VXLAN interfaces.

C.

FortiSwitch devices configured with NAT disabled.

D.

FortiSwitch devices that have the required internal hardware for this configuration.

E.

FortiSwitch and FortiGate devices configured with IPsec interfaces.

Buy Now
Questions 14

Refer to the exhibit.

14

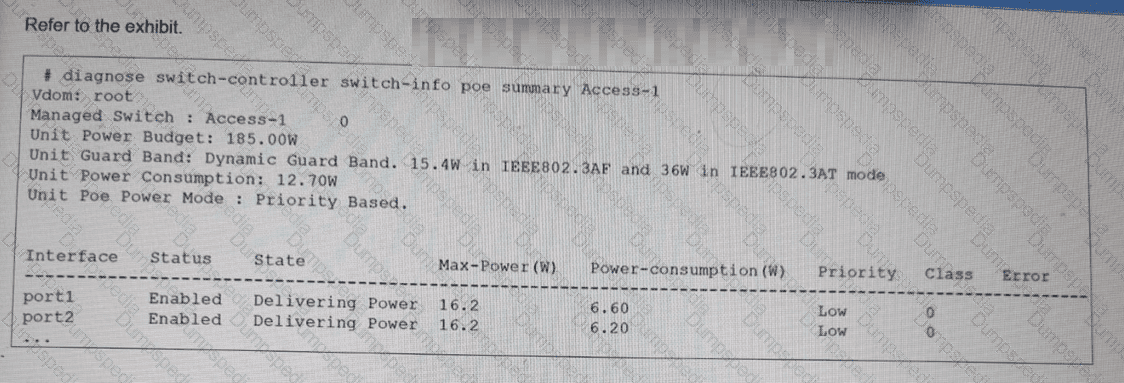
The FortiSwitch CLI output of the diagnose switch-controller switch-info poe summary command for the switch Access-1 is shown. It shows that two ports have Power over Ethernet (PoE) enabled and are already in use. What is the most important consideration if you want to connect additional PoE devices to FortiSwitch? (Choose one answer)

Options:

A.

All plugged devices use the same PoE standard: 802.3af/at.

B.

The FortiSwitch model supports the number of PoE devices that you want to connect.

C.

The PoE power mode matches the PoE standard of the device.

D.

The total PoE consumption must not exceed the FortiSwitch power budget.

Buy Now
Questions 15

Refer to the diagnostic output:

15

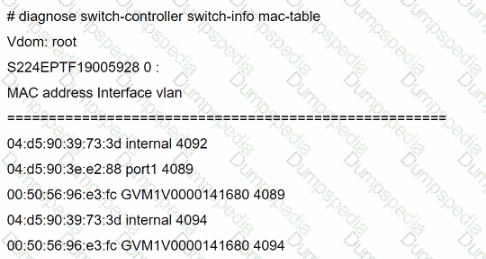
Two entries in the exhibit show that the same MAC address has been used in two different VLANs. Which MAC address is shown in the above output?

Options:

A.

It is a MAC address of FortiLink interface on FortiGate.

B.

It is a MAC address of a switch that accepts multiple VLANs.

C.

It is a MAC address of an upstream FortiSwitch.

D.

It is a MAC address of FortiGate in HA configuration.

Buy Now
Questions 16

Which statement about the IGMP snooping querier when enabled on a VLAN is true?

Options:

A.

Active multicast receiver entries are aging on each IGMP query sent on the VLAN

B.

IGMP reports on the VLAN are forwarded to all switch ports.

C.

The setting can only be enabled using the FortiSwitch CLI.

D.

All other indirectly connected switches will be unable to get IGMP multicast traffic.

Buy Now
Questions 17

FortiGate is unable to establish a tunnel with the FortiSwitch device it is supposed to manage Based on the debug output shown in the exhibit, what is the reason for the failure?

Options:

A.

The handshake process timed out before FortiSwitch responded.

B.

DTLS client hello had the incorrect pre-shared key.

C.

The CAPWAP tunnel failed to come up due to a mismatch in time.

D.

FortiSwitch has disabled FortiLink and is only managed as a standalone.

Buy Now
Questions 18

In which two ways can you assign a FortiSwitch port to a VDOM using a multi-tenancy setup? (Choose two answers)

Options:

A.

Assign the switch port to a VLAN on FortiGate and perform VDOM mapping.

B.

Create a virtual port pool on the FortiGate CLI.

C.

Assign a port to a VDOM directly on the managed FortiSwitch.

D.

Switch the FortiLink interface to the target VDOM.

Buy Now
Questions 19

Refer to the exhibit.

19

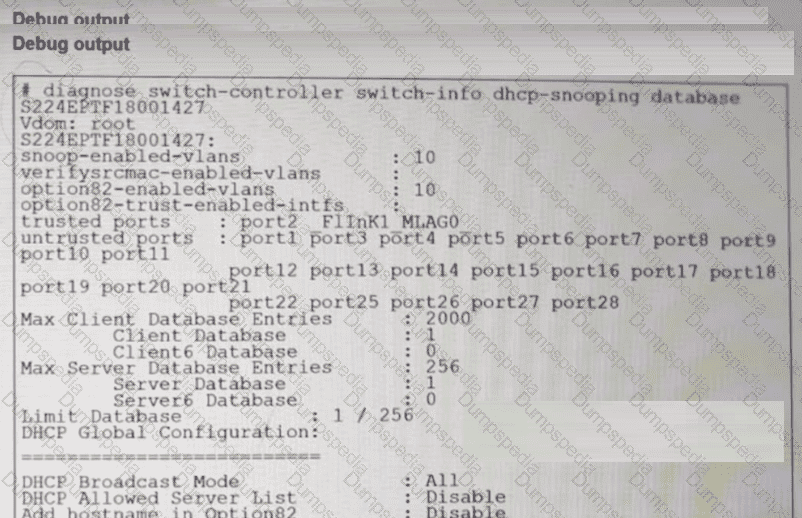
After reviewing the CLI command output, which two conclusions can you make about the Dynamic Host Configuration Protocol (DHCP) snooping configuration? (Choose two answers)

Options:

A.

DHCP snooping is disabled globally.

B.

All ports are untrusted, except port2.

C.

Option 82 is enabled on VLAN 10.

D.

DHCP broadcasts are not restricted.

Buy Now
Questions 20

You are designing a FortiSwitch backbone where every FortiSwitch device must connect to every other FortiSwitch for maximum redundancy. To maintain connectivity while preventing loops, which protocol or feature must you configure on the switches? (Choose one answer)

Options:

A.

Multichassis link aggregation group (MCLAG)

B.

Spanning Tree Protocol (STP)

C.

Full mesh high availability (HA)

D.

Link aggregation group (LAG)

Buy Now
Questions 21

What does the switchauto-networksetting control on FortiSwitch? (Choose one answer)

Options:

A.

The automatic VLAN assignment based on connected devices

B.

The automatic discovery of the FortiGate- > FortiLink interface

C.

The root bridge priority for Multiple Spanning Tree Protocol (MSTP)

D.

Whether the FortiSwitch can be managed by FortiManager

Buy Now
Questions 22

You are deploying a small office network with a single FortiGate and a single FortiSwitch. The office currently has moderate traffic, but the IT team expects the network to grow in the near future, adding more FortiSwitch devices and endpoints. Which FortiLink configuration should you deploy to provide the best combination of current performance and scalability for future growth? (Choose one answer)

Options:

A.

Configure FortiLink using hardware-based switch interfaces.1

B.

Configure FortiLink using software-based switch interfaces.

C.

Configure FortiLink as a link aggregation group (LAG) interface.

D.

Configure FortiLink as a multichassis LAG (MCLAG) interface.2

Buy Now
Questions 23

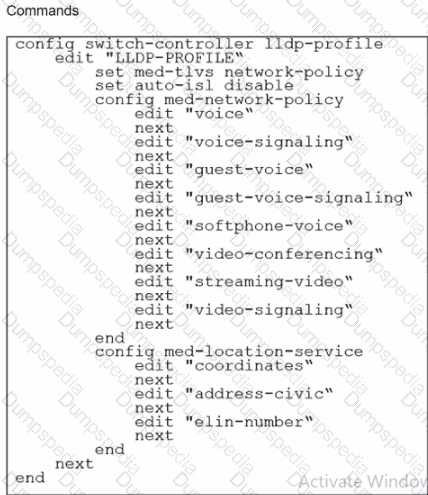
Refer to the exhibit.

23

The profile shown in the exhibit is assigned to a group of managed FortiSwitch ports, and these ports are connected to endpoints which are powered by PoE.

Which configuration action can you perform on the LLDP profile to cause these endpoints to exchange PoE information and negotiate power with the managed FortiSwitch?

Options:

A.

Create new a LLDP-MED application type to define the PoE parameters.

B.

Assign a new LLDP profile to handle different LLDP-MED TLVs.

C.

Define an LLDP-MED location ID to use standard protocols for power.

D.

Add power management as part of LLDP-MED TLVs to advertise.

Buy Now
Questions 24

Which two statements about VLAN assignments on FortiSwitch ports are true? (Choose two.)

Options:

A.

Configure a native VLAN on the FortiLink

B.

Assign an IP address and subnet mask to FortiSwitch VLANs

C.

Only assign one native VLAN on a port

D.

Assign untagged VLANs using FortiGate CLI

Buy Now
Questions 25

You are configuring VLANs on a FortiSwitch device managed by FortiGate. Which two statements accurately describe VLAN assignment requirements and behavior on FortiSwitch ports? (Choose two answers)

Options:

A.

Untagged defines the list of VLANs that are allowed on the port for both ingress and egress traffic.

B.

Untagged VLAN applies to egress traffic only.

C.

You can assign only one native VLAN on a port.

D.

VLAN assignments must be configured directly on the FortiSwitch.

Buy Now
Questions 26

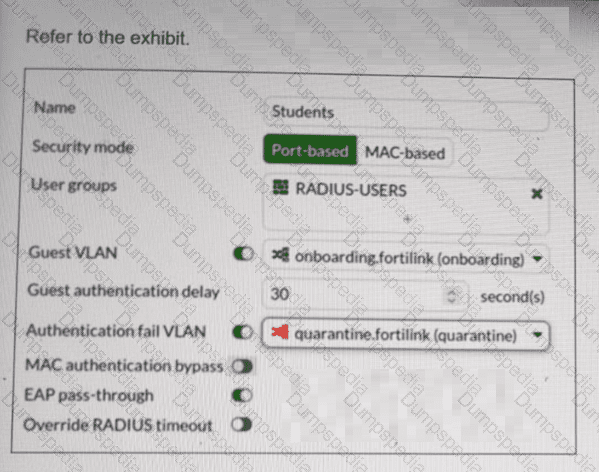
Refer to the exhibit.

26

FortiSwitch 802.1X port security configuration is shown. A user connects their laptop to the port and attempts to authenticate using 802.1X, but enters the wrong credentials multiple times. What will the result to the device be? (Choose one answer)

Options:

A.

The device will be placed into the VLAN quarantine.

B.

The port will shut down for security reasons.

C.

The device will be placed into the VLAN onboarding.

D.

The device will be assigned to the default management VLAN.

Buy Now
Questions 27

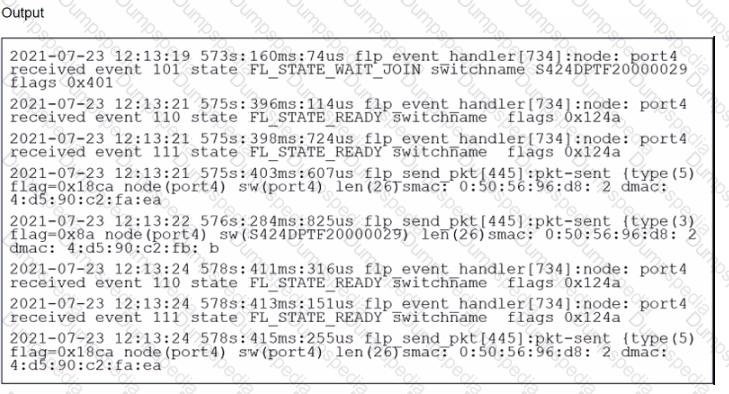
Refer to the exhibit.

27

Which two statements best describe what is displayed in the FortiLink debug output shown in the exhibit? (Choose two.)

Options:

A.

FortiSwitch is sending FortiLink heartbeats to FortiGate.

B.

FortiSwitch is discovered and authorized by FortiGate.

C.

FortiSwitch is in a waiting state to join the stack group on FortiGate.

D.

FortiSwitch is ready to push its new hostname to FortiGate.

Buy Now
Questions 28

Which two statements about 802.1X authentication on FortiSwitch ports are true? (Choose two.)

Options:

A.

All hosts behind an authenticated port are allowed access after a successful authentication.

B.

A security policy is used to apply 802.1 authentication on a port.

C.

A local user database must be used to authenticate devices using the 802.1X authentication protocol.

D.

All devices connecting to FortiSwitch must support 802.1X authentication.

Buy Now
Questions 29

Which two are valid traffic processing actions that a FortiSwitch access control list (ACL) can apply to matching traffic? (Choose two answers)

Options:

A.

Redirect frames to another port.

B.

Assign traffic to a high-priority egress queue.

C.

Encrypt frames.

D.

Drop frames.

Buy Now
Questions 30

(Full question statement start from here)

What is one key advantage of using a sniffer profile on FortiSwitch compared to using the sniffer command? (Choose one answer)

Options:

A.

It allows packet capture on all switch ports without limitations.

B.

It eliminates the need to use access control lists (ACLs) or port mirroring for analysis.

C.

It automatically filters irrelevant traffic types.

D.

It automatically decrypts SSL/TLS traffic for full packet inspection.

Buy Now
Questions 31

On supported FortiSwitch models, which access control list (ACL) stage is recommended for applying actions before the switch performs any layer 2 or layer 3 processing? (Choose one answer)

Options:

A.

Ingress

B.

Forwarding

C.

Egress

D.

Prelookup

Buy Now
Questions 32

You are configuring FortiSwitch to perform layer 3 inter-VLAN routing while managed by FortiGate over FortiLink. On supported hardware models, FortiSwitch can offload routing decisions for better performance.1How does FortiSwitch perform routing between VLANs? (Choose one answer)

Options:

A.

By using a hardware forwarding table (FIB) programmed into ASIC.

B.

By supporting only dynamic routing protocols in hardware.

C.

By disabling routing when managed by FortiGate.

D.

By relying entirely on the CPU in software.

Buy Now
Questions 33

What are two ways in which automatic MAC address quarantine works on FortiSwitch? (Choose two.)

Options:

A.

FortiSwitch supports only by VLAN quarantine mode.

B.

FortiGate applies the quarantine-related configuration only on FortiGate.

C.

FortiAnalyzer with a threat detection services license is required.

D.

MAC address quarantine can be enabled through the FortiGate CLI only.

Buy Now
Questions 34

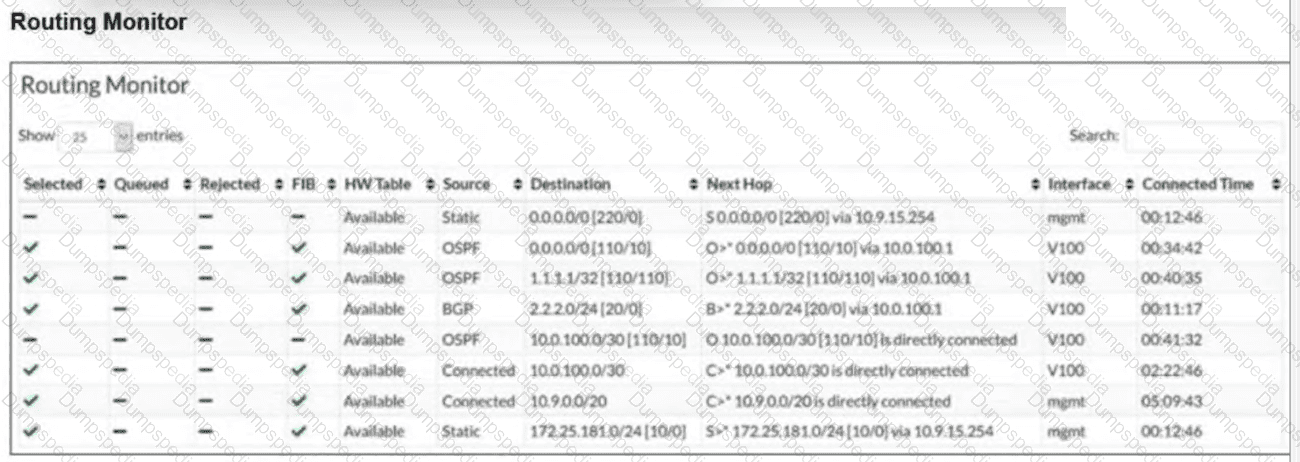
Refer to the exhibit.

34

and an OSPF route with destination 0.0.0.0/0 [110/10]. The OSPF route is marked with a checkmark in the FIB column, while the Static route has a dash.]

The routing monitor displays multiple route entries, but only some are installed in the forwarding information base (FIB). After analyzing the two route entries with the destination 0.0.0.0/0, which statement correctly describe why one of these routes is not installed in the FIB? (Choose one answer)
Options:

A.

The OSPF route has a higher metric, making it less preferred than the static route.

B.

The interface V100 for the OSPF route is down, preventing its installation.

C.

The OSPF route with a lower administrative distance is preferred over the static route.

D.

The two routes have identical destination prefixes, causing a conflict where only one is selected.

Buy Now
Exam Code: NSE5_FSW_AD-7.6
Exam Name: Fortinet NSE 5 - FortiSwitch 7.6 Administrator
Last Update: Sep 28, 2026
Questions: 114

PDF + Testing Engine

$51.42 $171.4

Testing Engine

$38.57 $128.55

PDF (Q&A)

$42.85 $142.82