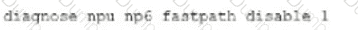
Weekend Sale Special - Limited Time 70% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: 70xmasdy

Welcome To DumpsPedia

NSE7_FSN_AR-7.6 Sample Questions Answers

Questions 4

What are two functions of automation stitches? (Choose two.)

Options:

A.

You can configure automation stitches to run diagnostic commands and attach the results to an email message when CPU or memory usage exceeds specified thresholds.

B.

You can configure automation stitches to modify packet headers and payloads if specific traffic triggers an anomaly IPS event.

C.

You can configure automation stitches to insert a delay between actions if the automation stitches are set to execute actions in parallel.

D.

You can configure automation stitches to take parameters from previous actions as input for the next action if the automation stitches are set to execute actions in sequence.

Buy Now
Questions 5

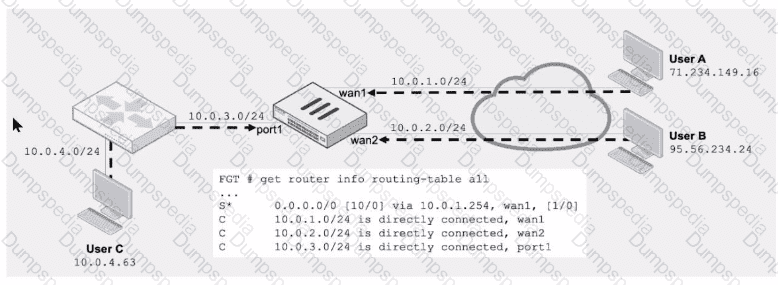
Refer to the exhibit.

5

Assuming a default configuration, which three statements are true? (Choose three.)

Options:

A.

Strict RPF is enabled by default.

B.

User B: Fail. There is no route to 95.56.234.24 .

C.

User A: Pass. The default static route through wan1 passes the RPF check regardless of the source IP address.

D.

User B: Pass. FortiGate will use asymmetric routing using wan1 to reply to traffic for 95.56.234.24.

E.

User C: Fail. There is no route to 10.0.4.63 using port1 in the touting table.

Buy Now
Questions 6

In which two ways does FortiGate utilize the Internet Service Database (ISDB) within firewall policies and SD-WAN rules? (Choose two.)

Options:

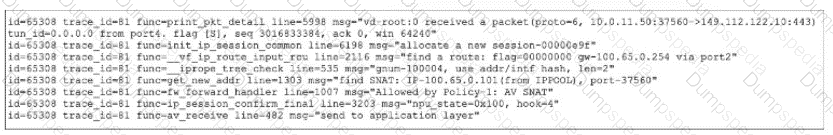
A.

The ISDB limits access by URL and domain.

B.

The ISDB works in proxy mode only, allowing the analysis of packets at Layers 3 and 4 of the OSI model.

C.

FortiGate has a predefined list of IP addresses and ports for specific applications downloaded from FortiGuard.

D.

The ISDB can be used to block the IP addresses and ports of an application predefined by FortiGuard.

Buy Now
Questions 7

Consider the scenario where the server name indication (SNI) does not match either the common name (CN) or any of the subject alternative names (SAN) in the server certificate. Which two actions will FortiGate take when using the default settings for SSL certificate inspection? (Choose two answers)

Options:

A.

FortiGate uses the SNI from the user ' s web browser.

B.

FortiGate does not decrypt the traffic if the traffic is blocked by the web filter profile.

C.

FortiGate uses the CN information from the Subject field in the server certificate.

D.

FortiGate does not decrypt the traffic if the traffic is allowed by the web filter profile.

Buy Now
Questions 8

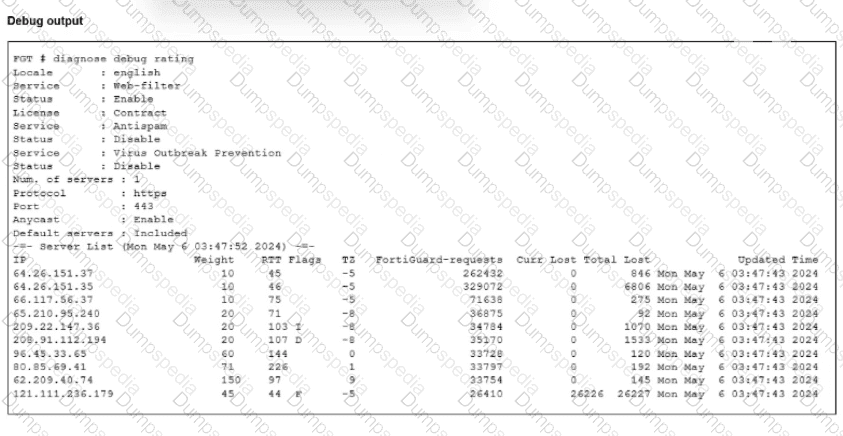
Exhibit.

8

Refer to the exhibit, which shows the output of a diagnose command.

What can you conclude about the debug output in this scenario?

Options:

A.

The first server provided to FortiGate when it performed a DNS query looking for a list of rating servers, was 121.111.236.179.

B.

There is a natural correlation between the value in the FortiGuard-requests field and the value in the Weight field.

C.

FortiGate used 64.26.151.37 as the initial server to validate its contract.

D.

Servers with a negative TZ value are less preferred for rating requests.

Buy Now
Questions 9

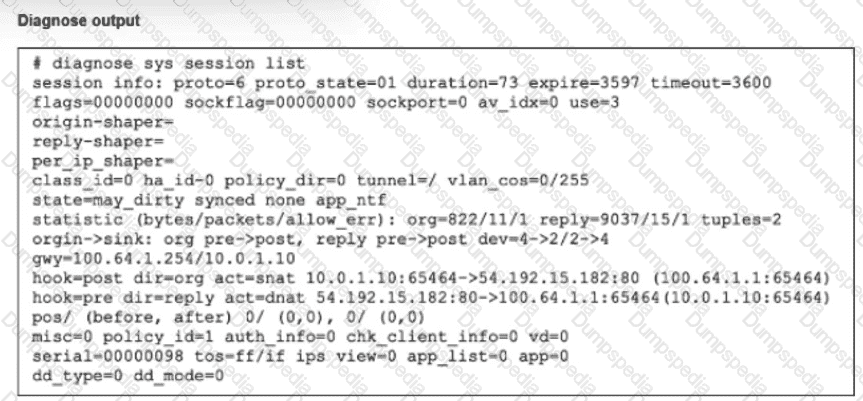
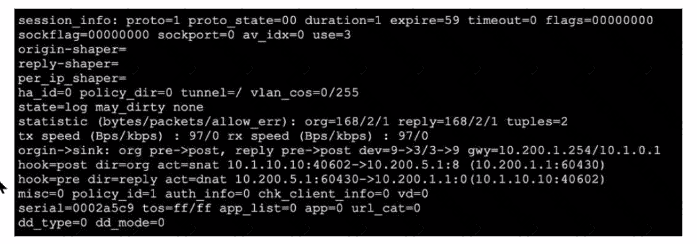
Refer to the exhibit, which shows a session entry.
9

Which statement about this session is true?

Options:

A.

Return traffic to the initiator is sent to 10.1.0.1.

B.

Return traffic to the initiator is sent lo 10.200.1.254.

C.

It is an ICMP session from 10.1.10.10 to 10.200.1.1.

D.

It is an ICMP session from 10.1.10.1 to 10.200.5.1.

Buy Now
Questions 10

Which two statements about Security Fabric communications are true? (Choose two.)

Options:

A.

FortiTelemetry and Neighbor Discovery both operate using TCP.

B.

The default port for Neighbor Discovery can be modified.

C.

FortiTelemetry must be manually enabled on the FortiGate interface.

D.

By default, the downstream FortiGate establishes a connection with the upstream FortiGate using TCP port 8013.

Buy Now
Questions 11

Refer to the exhibit.

11

The administrator did not override the FortiGuard FODN or IP address in the FortiGate configuration

Which IP address did FortiGate get when resolving the servicem,fortiguard.net name?

Options:

A.

208.91.112.194

B.

209.22.147.36

C.

64.26.151.37

D.

96.45.33.65

Buy Now
Questions 12

What is the diagnose test application ipsmonitor 5 command used for? (Choose one answer)

Options:

A.

To disable the IPS engine

B.

To provide information regarding IPS sessions

C.

To restart all IPS engines and monitors

D.

To enable IPS bypass mode

Buy Now
Questions 13

Refer to the exhibits.

Exhibit — Interface configuration and FortiGate routing table

Video exhibit showing port2 preserve-session-route configuration and the FortiGate routing table with two default routes.

The administrator increases the member priority on port2 to 20.

Assuming the route egressing port2 is still valid, upon configuration changes and the receipt of new packets, which two actions does FortiGate perform on existing sessions established over port2? (Choose two.)

Options:

A.

FortiGate continues routing all existing sessions over port2.

B.

FortiGate routes new sessions over port1.

C.

FortiGate updates the gateway information of the sessions with source network address translation (SNAT) so that they use port1 instead of port2.

D.

FortiGate flags all sessions as dirty.

E.

FortiGate flags all source network address translation (SNAT) sessions as dirty only if the administrator has assigned an IP pool to the firewall policies with NAT.

Buy Now
Questions 14

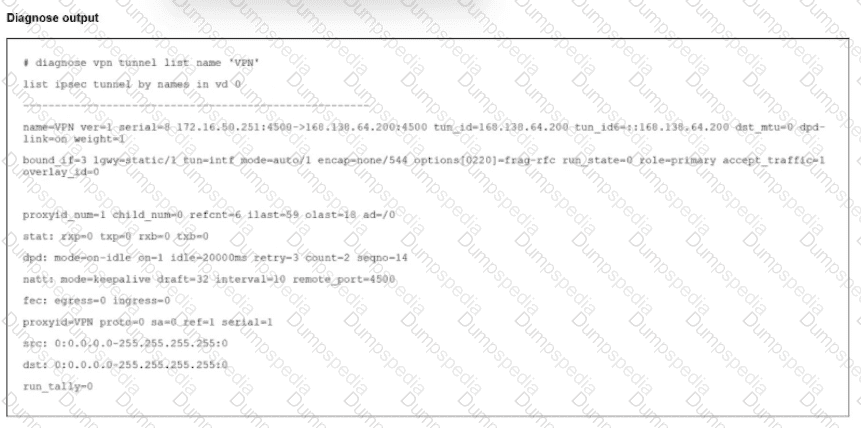
Refer to the exhibit.

14

The output of the command diagnose vpn tunnels liar is shown.

Which two statements accurately describe the status of the tunnel? (Choose two.)

Options:

A.

Phase 2 is down

B.

Phase 1 is down.

C.

There is currently no traffic traversing the tunnel

D.

Both Phase 1 and Phase 2 were negotiated successfully.

Buy Now
Questions 15

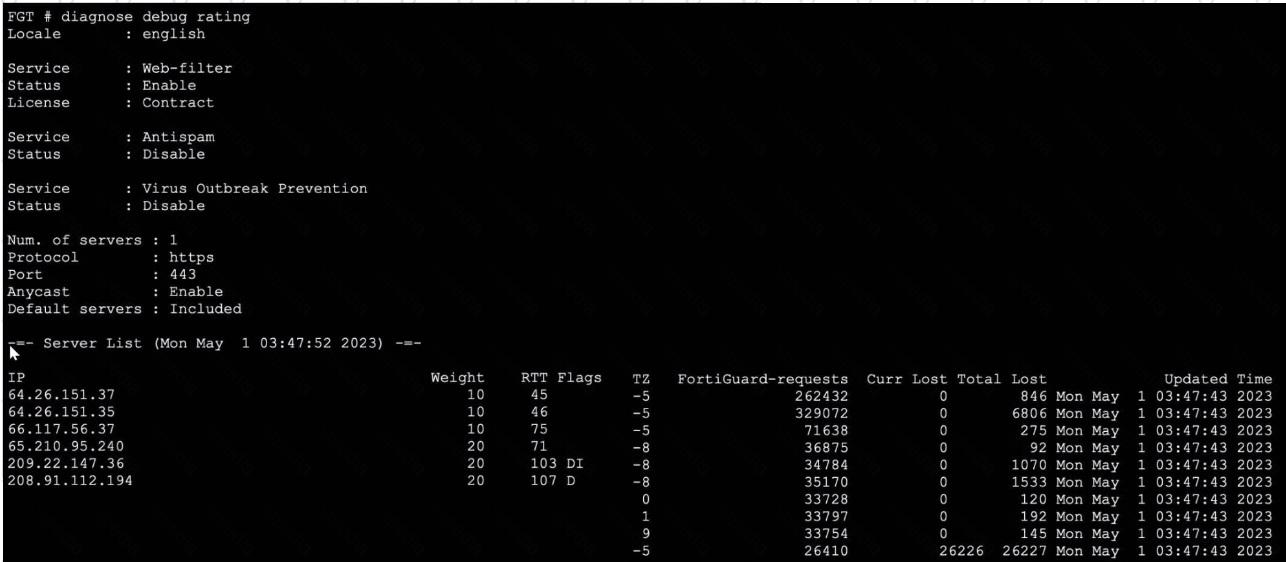
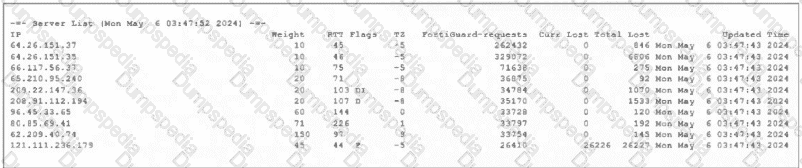
Refer to the exhibit, which shows the partial output of command diagnose debug rating.
15

In this exhibit, which FDS server will the FortiGate algorithm choose?

Options:

A.

66.117.56.37

B.

208.91.112.194

C.

209.22.147.36

D.

64.26.151.37

Buy Now
Questions 16

You want to harden the SSL/SSH inspection profile for access to HTTPS web servers.

Which two configuration changes allow you to remove vulnerabilities? (Choose two answers.)

Options:

A.

Set unsupported-ssl-version to block.

B.

Set Server certificate SNI check to Enable.

C.

Set Untrusted SSL certificates to Ignore.

D.

Set min-allowed-ssl-version to ssl-3.0.

Buy Now
Questions 17

Refer to the exhibit.

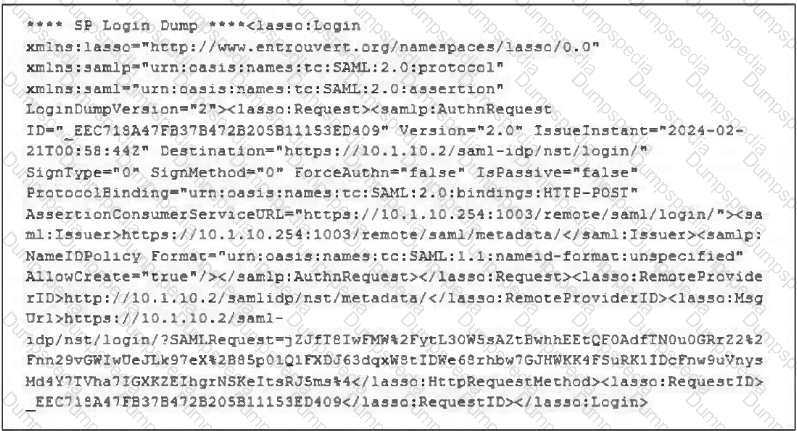
The exhibit shows the output from using the command diagnose debug application samld -1 to diagnose a SAML connection.
17

Based on this output, what can you conclude?

Options:

A.

Active Directory is used for authentication.

B.

The authentication request is for an SSL VPN connection.

C.

The IdP IP address is 10.1.10.254.

D.

The IdP IP address is 10.1.10.2.

Buy Now
Questions 18

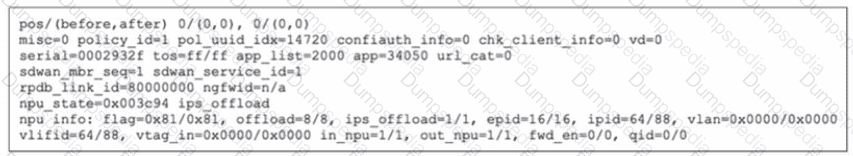
Refer to the exhibit.

18

The partial output of a session table entry is shown.

Which two statements about the output shown in the exhibit are correct? (Choose two.)

Options:

A.

NP7 is handling offloading of this session.

B.

The traffic matches Policy ID 1.

C.

The session has been offloaded.

D.

The traffic is tagged for a VLAN interface.

Buy Now
Questions 19

You use the FortiManager SD-WAN overlay orchestrator to prepare an SD-WAN deployment. Using information provided through the SD-WAN overlay template wizard, FortiManager creates templates that are ready to install on the spoke and hub devices.

Which three templates are created by the SD-WAN overlay orchestrator for a spoke device? (Choose three answers.)

Options:

A.

Rules template

B.

CLI template

C.

IPsec tunnel template

D.

BGP template

E.

Static route template

Buy Now
Questions 20

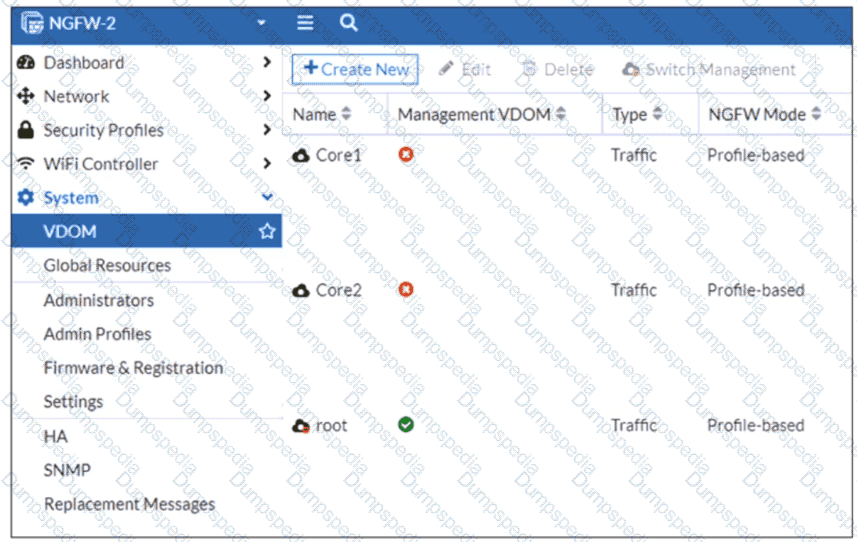
Refer to the exhibit.

20

The VDOM configuration on a FortiGate device is shown. You discover that web filtering stopped working in Core1 and Core2 after a maintenance window.

What are two reasons why web filtering stopped working? (Choose two answers.)

Options:

A.

The root VDOM does not have access to FortiManager in a closed network.

B.

The root VDOM does not have access to any valid public Fortinet Distribution Network (FDN) server.

C.

The Core1 and Core2 VDOMs must also be enabled as management VDOMs to receive FortiGuard updates.

D.

The root VDOM does not use a VDOM link to connect with the Core1 and Core2 VDOMs.

Buy Now
Questions 21

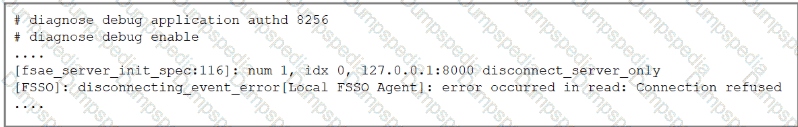
Refer to the exhibit showing a debug output.
21

An administrator deployed FSSO in DC Agent Mode but FSSO is failing on FortiGate. Pinging FortiGate from where the collector agent is deployed is successful.

The administrator then produces the debug output shown in the exhibit.

What could be causing this error message?

Options:

A.

The TCP port 445 is blocked between FortiGate and collector agent.

B.

The collector agent preshared password is mismatched.

C.

The FortiGate cannot resolve the active directory server name.

D.

The FortiGate and the collector agent are using different TCP ports.

Buy Now
Questions 22

When you deploy SD-WAN, you can choose from several common designs. Each design best applies to specific contexts.

Which two statements correctly associate a common SD-WAN design with its main indication or constraint? (Choose two.)

Options:

A.

Use remote breakout to centralize traffic inspection and limit local management requirements.

B.

Use a direct internet access (DIA) design to increase traffic security and allow local devices with limited capabilities.

C.

Use a standalone design for sites with only one WAN link to the cloud.

D.

Use a cloud on-ramp topology to improve the performance of cloud applications.

Buy Now
Questions 23

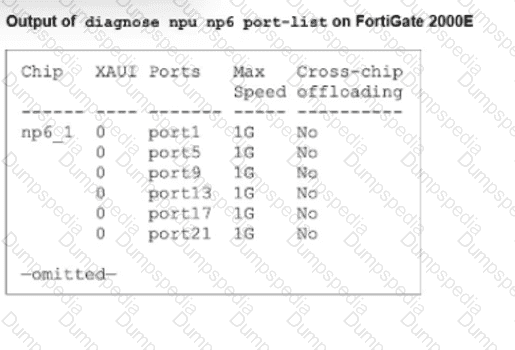
Refer to the exhibit.

23

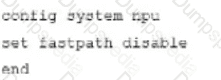
A partial output of diagnose npu up6 port-list on FortiGate 2000E is shown.

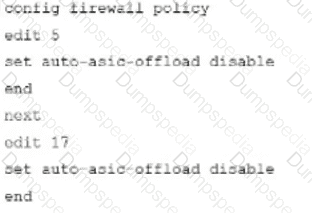
An administrator is unable to analyze traffic flowing between port1 and port17 using the diagnose sniffer command.

Which two commands allow the administrator to view the traffic? (Choose two.)

A)
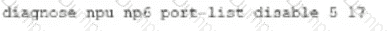
23

B)

23

C)

23

D)

23

Options:

A.

Option A

B.

Option B

C.

Option C

D.

Option D

Buy Now
Questions 24

In a transparent VDOM interface, what does the command set forward-domain < domain_ID > do?

Options:

A.

It allows the interface to access the configured administrative domain.

B.

It restricts the interface to managing traffic from only the specified VLAN, effectively segregating network traffic.

C.

It isolates traffic by assigning a broadcast domain to an interface, commonly using the VLAN ID as the domain ID.

D.

It assigns a unique domain ID to the interface, allowing it to operate across multiple VLANs within the same VDOM.

Buy Now
Questions 25

What can cause an IKEv2 tunnel to go down after it was initially brought up successfully?

Options:

A.

Mismatched traffic selectors (phase 2 / “quick-mode selectors”) were detected during the CREATE_CHILD_SA exchange.

B.

A mismatched proposal was detected during the IKE_AUTH exchange.

C.

A mismatched pre-shared key was detected during the IKE_AUTH exchange.

D.

A mismatched Diffie-Hellman group was detected during the IKE_SA_INIT exchange.

Buy Now
Questions 26

Which three conditions are required for two FortiGate devices to form an OSPF adjacency? (Choose three answers)

Options:

A.

OSPF link costs match.

B.

OSPF interface priority settings are unique.

C.

OSPF interface network types match.

D.

Authentication settings match.

E.

OSPF router IDs are unique.

Buy Now
Questions 27

What is an accurate description of LDAP authentication using the regular bind type?

Options:

A.

The regular bind requires the client to send the full distinguished name (ON).

B.

The regular bind type is the easiest bind type to configure on ForbOS.

C.

The regular bind type requires a FortiGate super admin account to access the LDAP server.

D.

It is not often used as a bind type

Buy Now
Questions 28

Which of the following regarding protocol states is true? (Choose one answer)

Options:

A.

proto_state=00 indicates that UDP traffic flows in both directions.

B.

proto_state=01 indicates an established TCP session.

C.

proto_state=10 indicates an established TCP session.

D.

proto_state=01 indicates one-way ICMP traffic.

Buy Now
Questions 29

Refer to the exhibit.

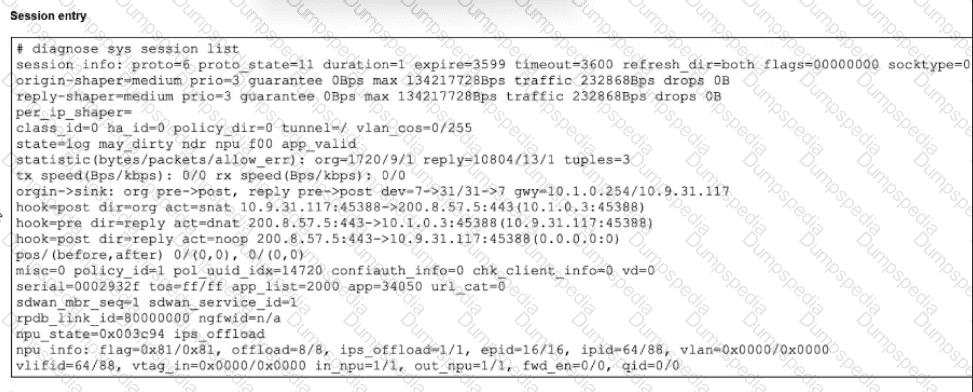
29

The exhibit shows a session entry. Which statement about this TCP session is true?

Options:

A.

The session will expire in one second.

B.

It is a TCP session from 10.9.31.117 to 10.1.0.3.

C.

The session is offloaded using NPU.

D.

Return traffic to the initiator is sent to 10.9.31.117.

Buy Now
Questions 30

Refer to the exhibits.

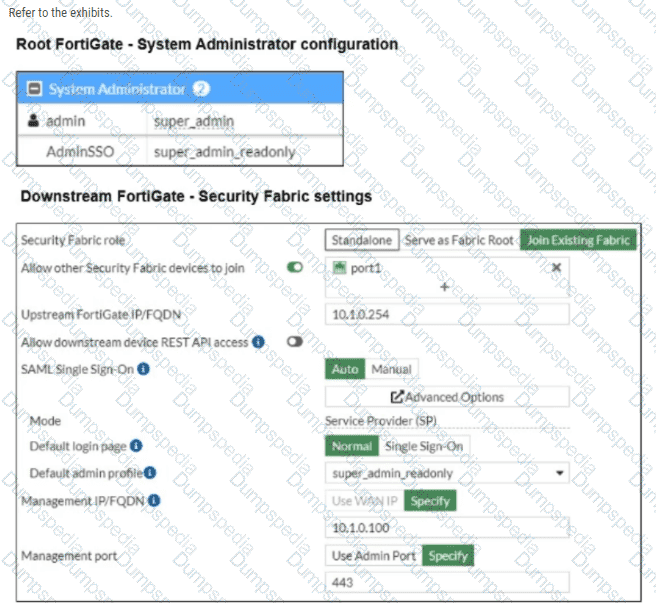
30

The system administrator settings configured on the root FortiGate and the Security Fabric settings configured on a downstream FortiGate are shown.

When prompted to sign in with Security Fabric to the downstream FortiGate, a user enters the single sign-on (SSO) provider credentials.

What happens next for the user?

Options:

A.

The user is redirected to the root FortiGate.

B.

The user accesses the downstream FortiGate with super_admin_readonly privileges.

C.

The user accesses the root FortiGate with AdminSSO privileges.

D.

The user receives an authentication failure message.

Buy Now
Questions 31

Refer to the exhibit.

31

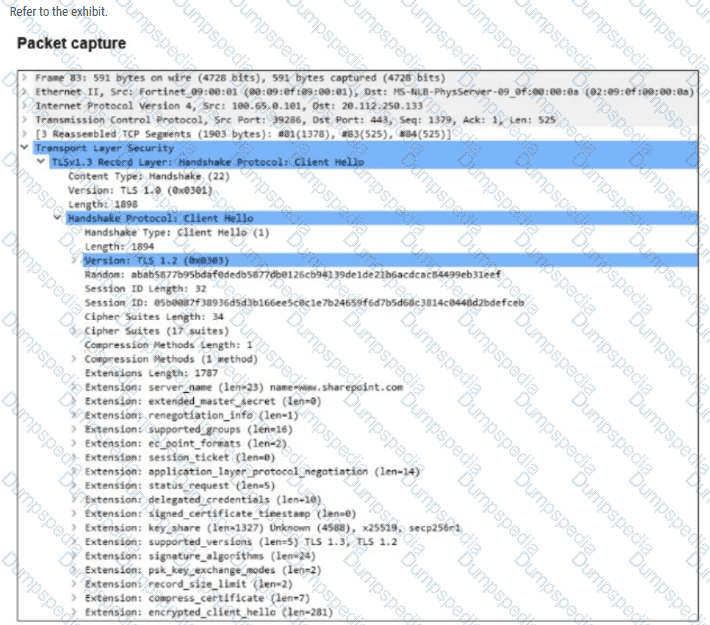
The packet capture output of a ClientHello message is shown.

You are updating a firewall policy that includes SSL certificate inspection. You are capturing packets from traffic passing through this firewall policy.

Which two statements about the packet capture are correct? (Choose two.)

Options:

A.

You can effectively apply an antivirus security profile to this traffic.

B.

You can effectively apply a web filtering profile to this traffic.

C.

The subject alternative name (SAN) is necessary to apply security profiles.

D.

The client supports only TLS versions 1.2 and 1.3.

Buy Now
Questions 32

What can cause an IKEv2 tunnel to go down after it was initially brought up successfully?

Options:

A.

A mismatched proposal was detected during the IKE_AUTH exchange.

B.

A mismatched Diffie-Hellman group was detected during the IKE_SA_INIT exchange.

C.

A mismatched pre-shared key was detected during the IKE_AUTH exchange.

D.

Mismatched quick-mode selectors were detected during the CREATE_CHILD_SA exchange.

Buy Now
Questions 33

In the context of SD-WAN, the terms underlay and overlay are commonly used to categorize links.

Which two statements about underlay and overlay links are correct? (Choose two.)

Options:

A.

A FortiLink interface is considered an underlay link.

B.

Overlay links provide routing flexibility.

C.

Only wired connections can be used as underlay links.

D.

Wireless connections can be used to build overlay links.

E.

A VLAN is a type of overlay link.

Buy Now
Questions 34

Refer to the exhibit.

34

Which two observations can you make about the web filter traffic captured using the flow tool? (Choose two.)

Options:

A.

The session is offloaded to the NPU.

B.

The firewall policy is configured with proxy-based inspection mode.

C.

The web filter profile is configured with proxy-based inspection mode.

D.

The HTTPS port is mapped to 443 in the SSL/SSH Inspection Profile

Buy Now
Questions 35

Refer to the exhibit.

35

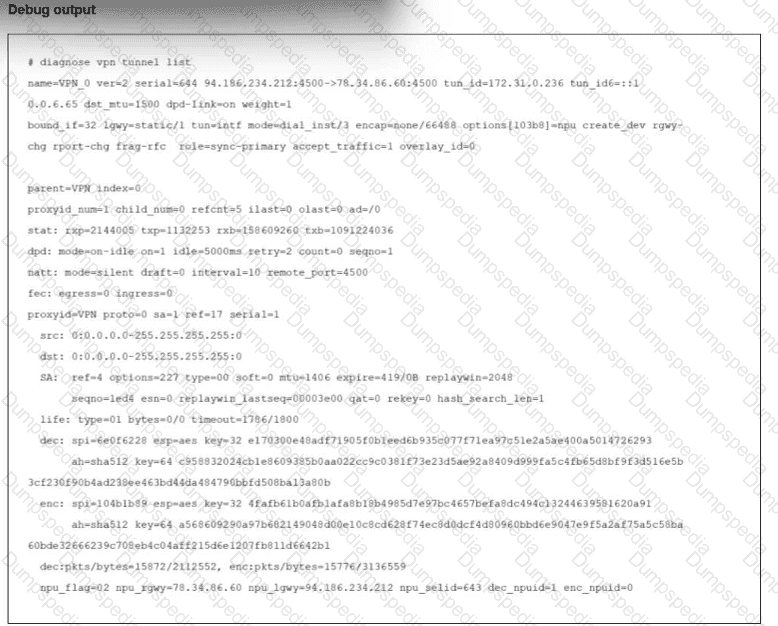
The output of the command diagnose vpn tunnel list is shown.

Reviewing the debug command, what is the current status of the traffic flowing through the tunnel?

Options:

A.

The outbound IPsec SA was copied to the NPU.

B.

NP6 is handling the offloading.

C.

The inbound and outbound IPsec SAs were copied to the NPU.

D.

The inbound IPsec SA was copied to the NPU.

Buy Now
Questions 36

During which phase of IKEv2 does the Diffie-Helman key exchange take place?

Options:

A.

IKE_Req_INIT

B.

Create_CHILD_SA

C.

IKE_Auth

D.

IKE_SA_INIT

Buy Now
Questions 37

What are three characteristics of the provisioning templates available on FortiManager? (Choose three.)

Options:

A.

Each template group can contain up to three IPsec tunnel templates.

B.

A CLI template can be of type CLI script or Perl script.

C.

A CLI template group can contain CLI templates of different types.

D.

CLI templates are applied in order, from top to bottom.

E.

A template group can include a system template and an SD-WAN template.

Buy Now
Questions 38

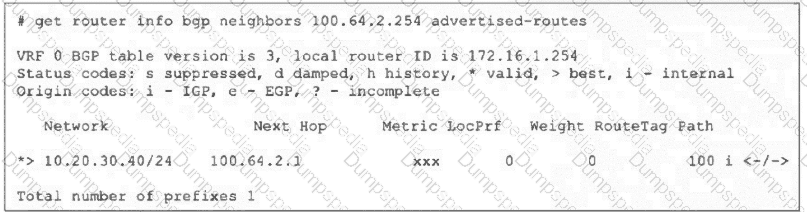
Refer to the exhibit, which shows the output of the command get router info bgp neighbors 100.64.2.254 advertised-routes.
38

What can you conclude from the output?

Options:

A.

The BGP state of the two BGP participants is OpenConfirm.

B.

The router ID of the neighbor is 100.64.2.254.

C.

The BGP neighbor is advertising the 10.20.30.40/24 network to the local router.

D.

The local router is advertising the 10.20.30.40/24 network to its BGP neighbor.

Buy Now
Questions 39

Which two statements about Security Fabric communications are true? (Choose two.)

Options:

A.

By default, the downstream FortiGate establishes a connection with the upstream FortiGate using TCP port 8013.

B.

FortiTelemetry must be manually enabled on the FortiGate interface.

C.

The default ports for FortiTelemetry and Neighbor Discovery can be modified.

D.

Security Fabric communication is enabled by default among all Fortinet devices.

Buy Now
Questions 40

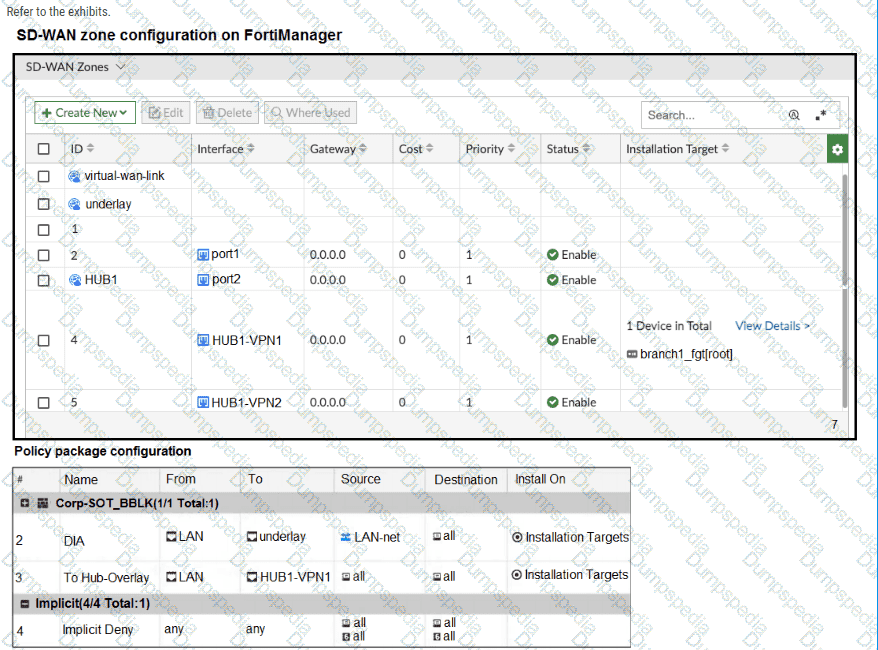
Refer to the exhibits.

40

The exhibits show the SD-WAN zone configuration of an SD-WAN template prepared on FortiManager and the policy package configuration.

When the administrator tries to install the configuration changes, FortiManager fails to commit.

What should the administrator do to fix the issue?
Options:

A.

Configure branch1_fgt as the installation target for policy 3.

B.

Configure HUB1 as the destination of policy 3.

C.

Configure a normalized interface for the IPsec tunnel HUB1-VPN1.

D.

Configure both HUB1-VPN1 and HUB1-VPN2 as the destination of policy 3.

Buy Now
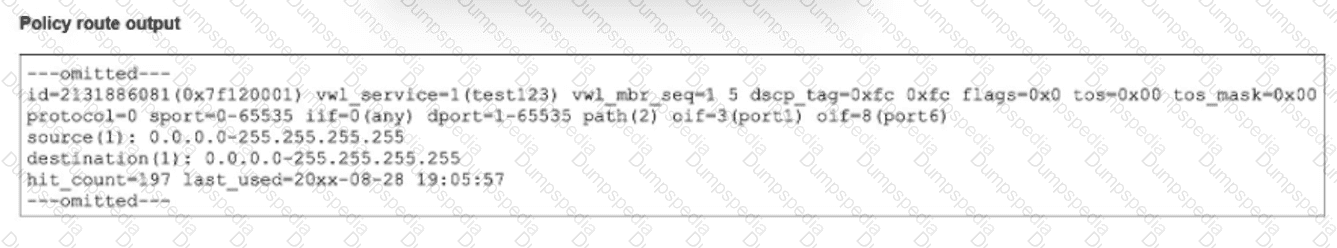
Questions 41

41

The output of a policy route table entry is shown.

Which type of policy route does the output show?

Options:

A.

A regular policy route, which is not associated with an active static route in the FIB

B.

An ISDB route

C.

An SD-WAN rule

D.

A regular policy route, which is associated with an active static route in the FIB

Buy Now
Questions 42

An administrator wants to capture encrypted phase 2 traffic between two FotiGate devices using the built-in sniffer.

If the administrator knows that there Is no NAT device located between both FortiGate devices, which command should the administrator run?

Options:

A.

diagnose sniffer packet any ' udp port 500 '

B.

diagnose sniffer packet any ' lp proto 50 '

C.

diagnose sniffer packet any ' udp port 4500 '

D.

diagnose sniffer packet any ' ah '

Buy Now
Questions 43

Refer to the exhibit.

43

The output of diagnose sys session list command is shown.

If the HA ID for the primary device is 9, what happens if the primary fails and the secondary becomes the primary?

Options:

A.

The session is synchronized with the secondary device, however, because application control is applied. the session is marked dirty and has to be reevaluated after failover.

B.

The session will be removed from the session table of the secondary device because the TCP session is not yet fully established.

C.

The session continues to permit traffic on the new primary device after failover. without requiring the client to restart the session with the server.

D.

The session state is preserved but the kernel will re-evaluate the session because the routing information will be flushed

Buy Now
Questions 44

Refer to the exhibit, which shows partial outputs from two routing debug commands.
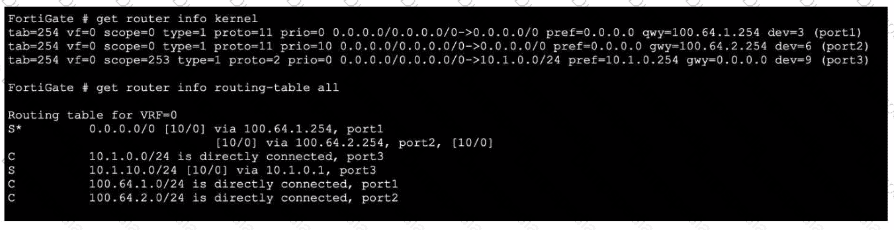
44

Which change must an administrator make on FortiGate to route web traffic from internal users to the internet, using ECMP?

Options:

A.

Set snat-route-change to enable.

B.

Set the priority of the static default route using port2 to 1.

C.

Set preserve-session-route to enable.

D.

Set the priority of the static default route using port1 to 10.

Buy Now
Questions 45

Exhibit.

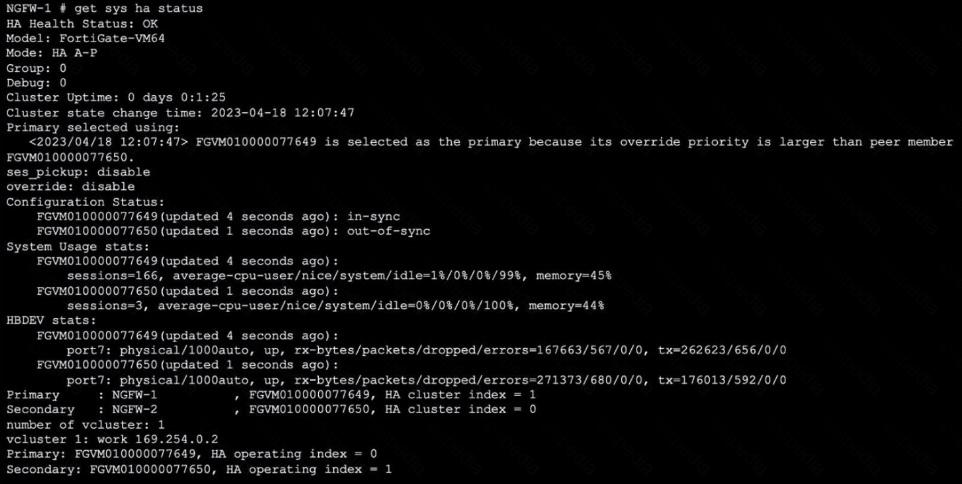
45

Refer to the exhibit, which shows the output of get system ha status.

NGFW-1 and NGFW-2 have been up for a week.

Which two statements about the output are true? (Choose two.)

Options:

A.

If a configuration change is made to the primary FortiGate at this time, the secondary will initiate a synchronization reset.

B.

If port 7 becomes disconnected on the secondary, both FortiGate devices will elect itself as primary.

C.

If FGVM...649 is rebooted. FGVM...650 will become the primary and retain that role, even after FGVM...649 rejoins the cluster.

D.

If no action is taken, the primary FortiGate will leave the cluster because of the current sync status.

Buy Now
Questions 46

You are checking an enterprise network and see a suspicious packet with the MAC address 00:09:0f:09:18:81.

Which two statements about the suspicious packet are correct? (Choose two.)

Options:

A.

The suspicious packet corresponds to a port with a physical index equal to 2.

B.

The suspicious packet is related to a cluster configured with the FortiGate Session Life Support Protocol (FGSP).

C.

The suspicious packet is related to a cluster that has VDOMs enabled.

D.

The suspicious packet is related to a cluster with a group-id value lower than 255.

Buy Now
Questions 47

Which two statements about an auxiliary session ate true? (Choose two.)

Options:

A.

With the auxiliary session selling disabled, only auxiliary sessions are offloaded.

B.

With the auxiliary session setting enabled. ECMP traffic is accelerated to the NP6 processor.

C.

With the auxiliary session setting enabled. Iwo sessions are created in case of routing change.

D.

With the auxiliary session setting disabled, for each traffic path. FortiGate uses the same auxiliary session.

Buy Now
Questions 48

Consider the scenario where the server name indication (SNI) does not match either the common name (CN) or any of the subject alternative names (SAN) in the server certificate.

Which action will FortiGate take when using the default settings for SSL certificate inspection?

Options:

A.

FortiGate uses the SNI from the user ' s web browser.

B.

FortiGate closes the connection because this represents an invalid SSL/TLS configuration.

C.

FortiGate uses the first entry listed in the SAN field in the server certificate.

D.

FortiGate uses the CN information from the Subject field in the server certificate.

Buy Now
Questions 49

Refer to the exhibit.

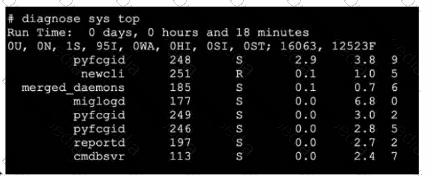
49

Which three pieces of information does the diagnose sys top command provide? (Choose three.)

Options:

A.

The miglogd daemon is running on CPU core ID 0.

B.

The diagnose sys top command has been running for 18 minutes.

C.

The miglogd daemon would be on top of the list, if the administrator pressed m on the keyboard.

D.

The cmdbsvr process is occupying 2.4% of the total user memory space.

E.

If the neweli daemon continues to be in the R state, it will need to be manually restarted.

Buy Now
Questions 50

In the SAML negotiation process, which section does the Identity Provider (IdP) provide the SAML attributes utilized in the authentication process to the Service Provider (SP)?

Options:

A.

SP Login dump

B.

Authentication Response

C.

Authentication Request

D.

Assertion dump

Buy Now
Questions 51

Which two protocol states indicate that traffic is bidirectional? (Choose two.)

Options:

A.

proto_state=01 for a TCP session.

B.

proto_state=01 for a UDP session.

C.

proto_state=05 for a TCP session.

D.

proto_state=00 for an ICMP session.

Buy Now
Questions 52

Refer to the exhibit.

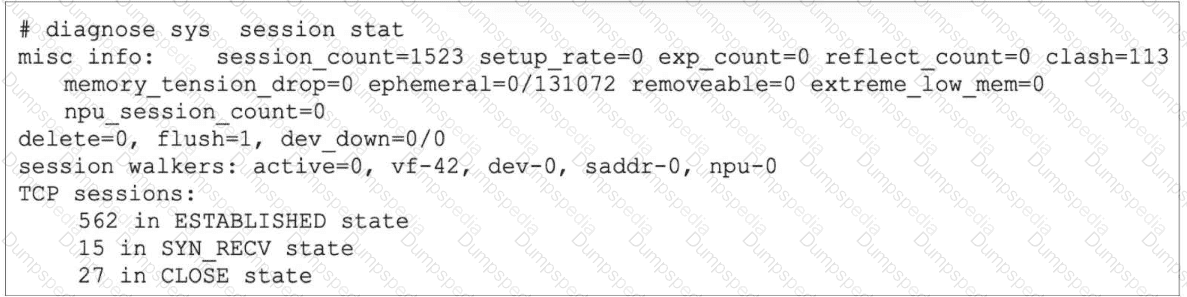
52

The partial output of diagnose sys session stat command is shown.

Which statement about the output shown in the exhibit is correct?

Options:

A.

113 sessions have been dropped because of memory page exhaustion.

B.

There have been 131072 recorded ephemeral sessions but there are no current ones.

C.

562 TCP sessions have their proto_state set to 01 if there is no inspection.

D.

27 sessions have expired but are still in the session table in case any out-of-order packets arrive.

Buy Now
Questions 53

Refer to the exhibit, which shows the output o! the BGP database.
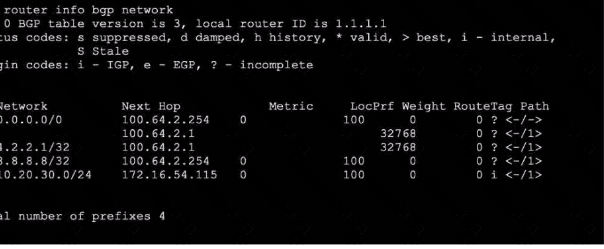
53

Which two statements are correct? (Choose two.)
Options:

A.

The advertised prefix of 10.20.30.0/24 was configured using the network command.

B.

The first four prefixes are being advertised using a legacy route advertisement.

C.

The advertised prefix of 10.20.30.0/24 is being advertised through the redistribution of another routing protocol.

D.

The output shows all prefixes advertised by all neighbors as well as the local router.

Buy Now
Exam Code: NSE7_FSN_AR-7.6
Exam Name: Fortinet NSE 7 - Secure Networking 7.6 Architect
Last Update: Nov 8, 2026
Questions: 177

PDF + Testing Engine

$51.42 $171.4

Testing Engine

$38.57 $128.55

PDF (Q&A)

$42.85 $142.82